Ticket 05 — Unauthorized Access Request
Ticket Summary
Taylor requested access to a Finance shared resource.
Because access to departmental resources was controlled through Active Directory security groups, the request required an authorization check before any permissions could be changed.
This scenario demonstrates role-based access control and least privilege in a service-desk environment.
User Request
Taylor submitted a service-desk request asking for access to the Finance shared resource.
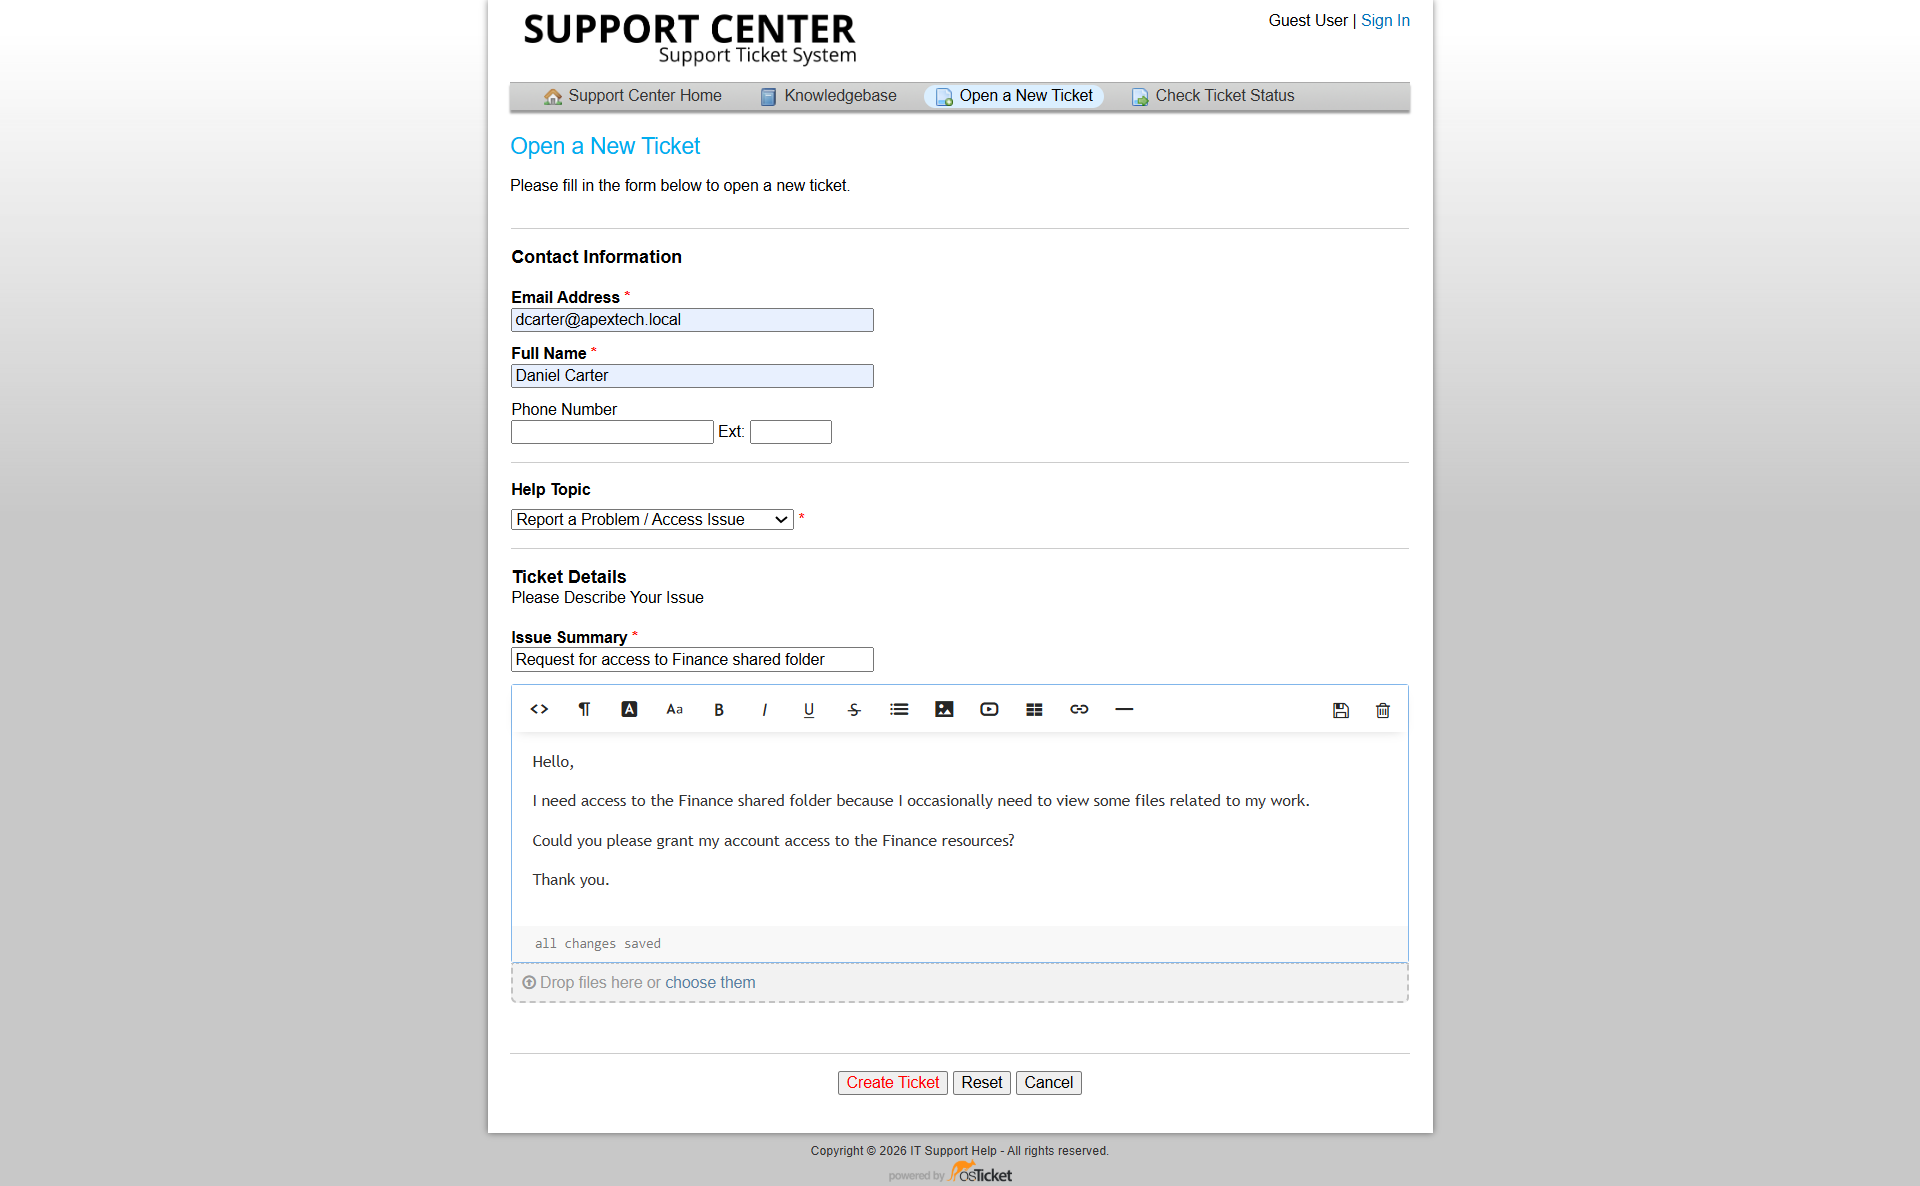
Taylor's Finance access request submitted through osTicket.
The request could not be approved based solely on the user's request. I first needed to determine whether Finance access was appropriate for Taylor's existing role.
Authorization Review
I reviewed Taylor's Active Directory group membership and the access model used by the Finance resource.
The first step was to test the requested resource.
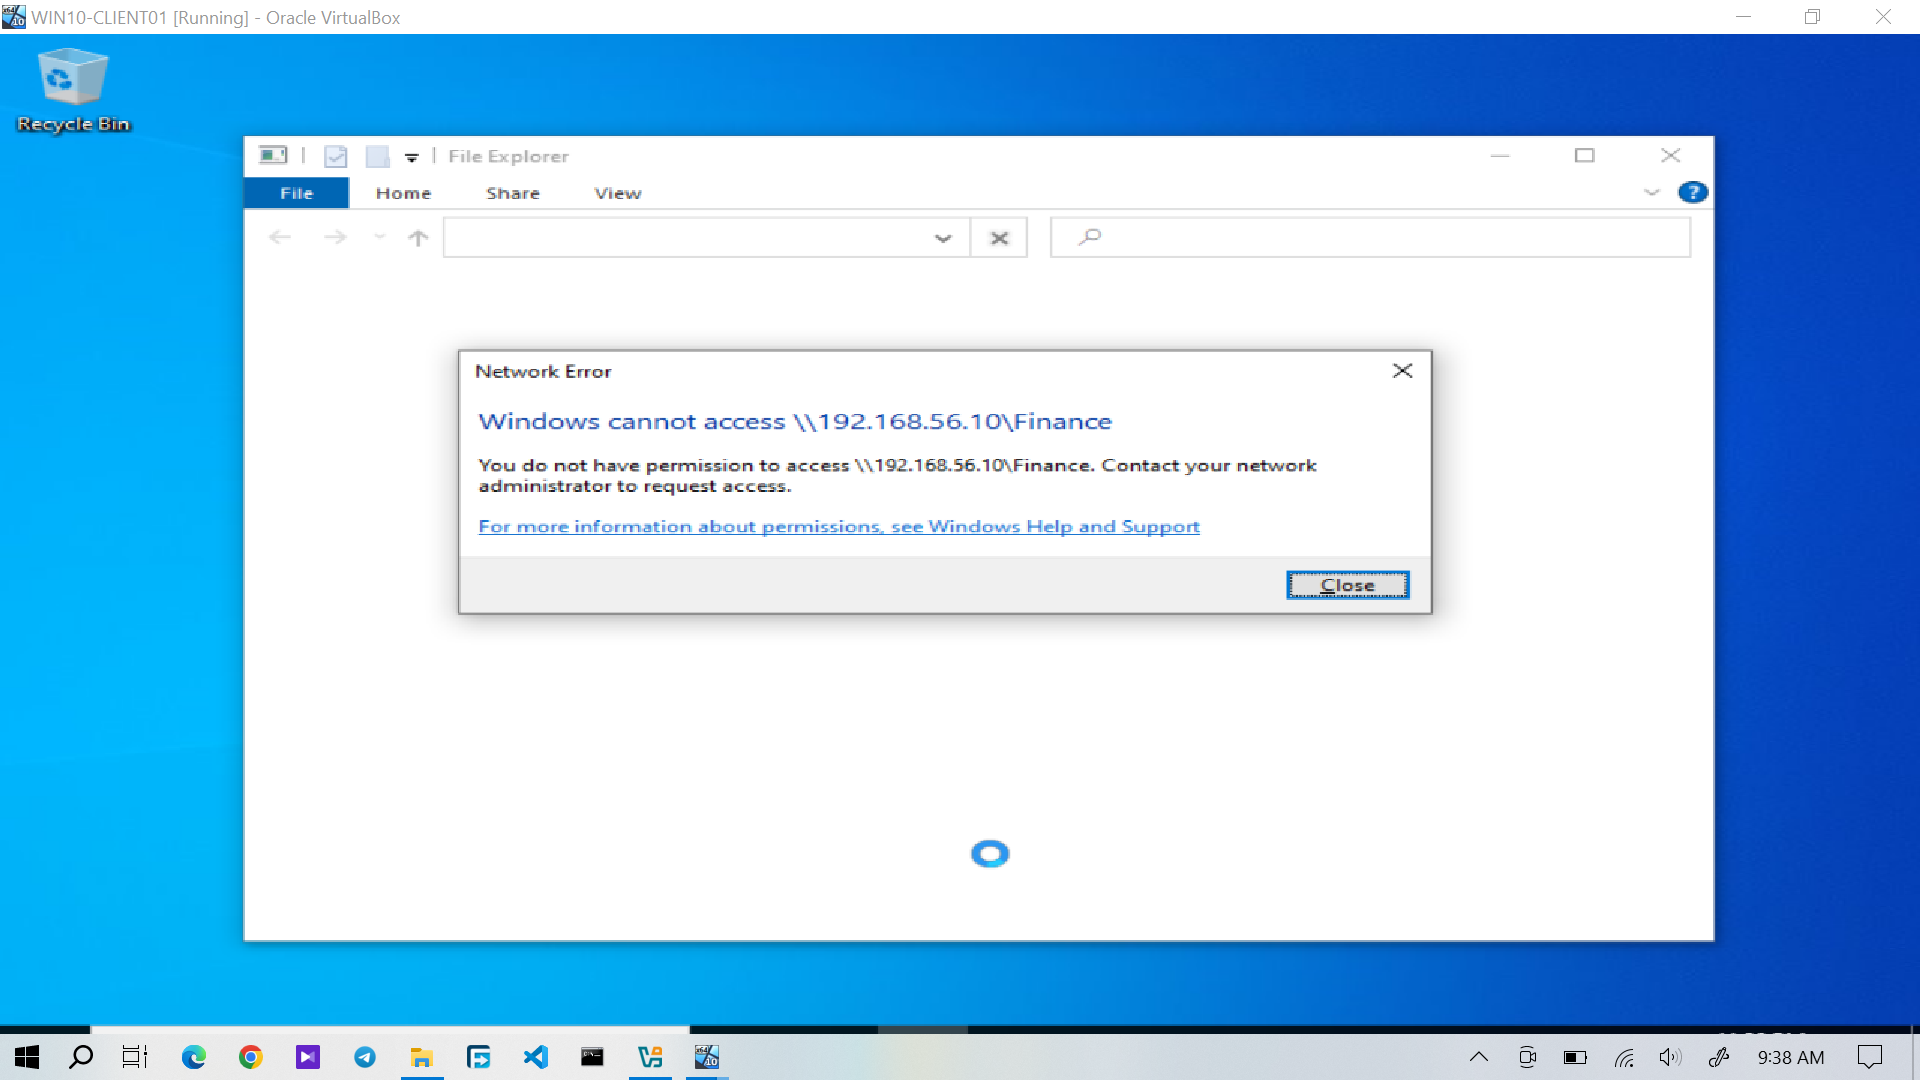
Taylor receiving an access denied result when attempting to access the Finance resource.
The denied access was expected based on the current authorization configuration. The next step was to determine whether that configuration was correct.
Reviewing Taylor's Group Membership
Taylor's Active Directory group membership was checked to identify the resources currently authorized for the account.
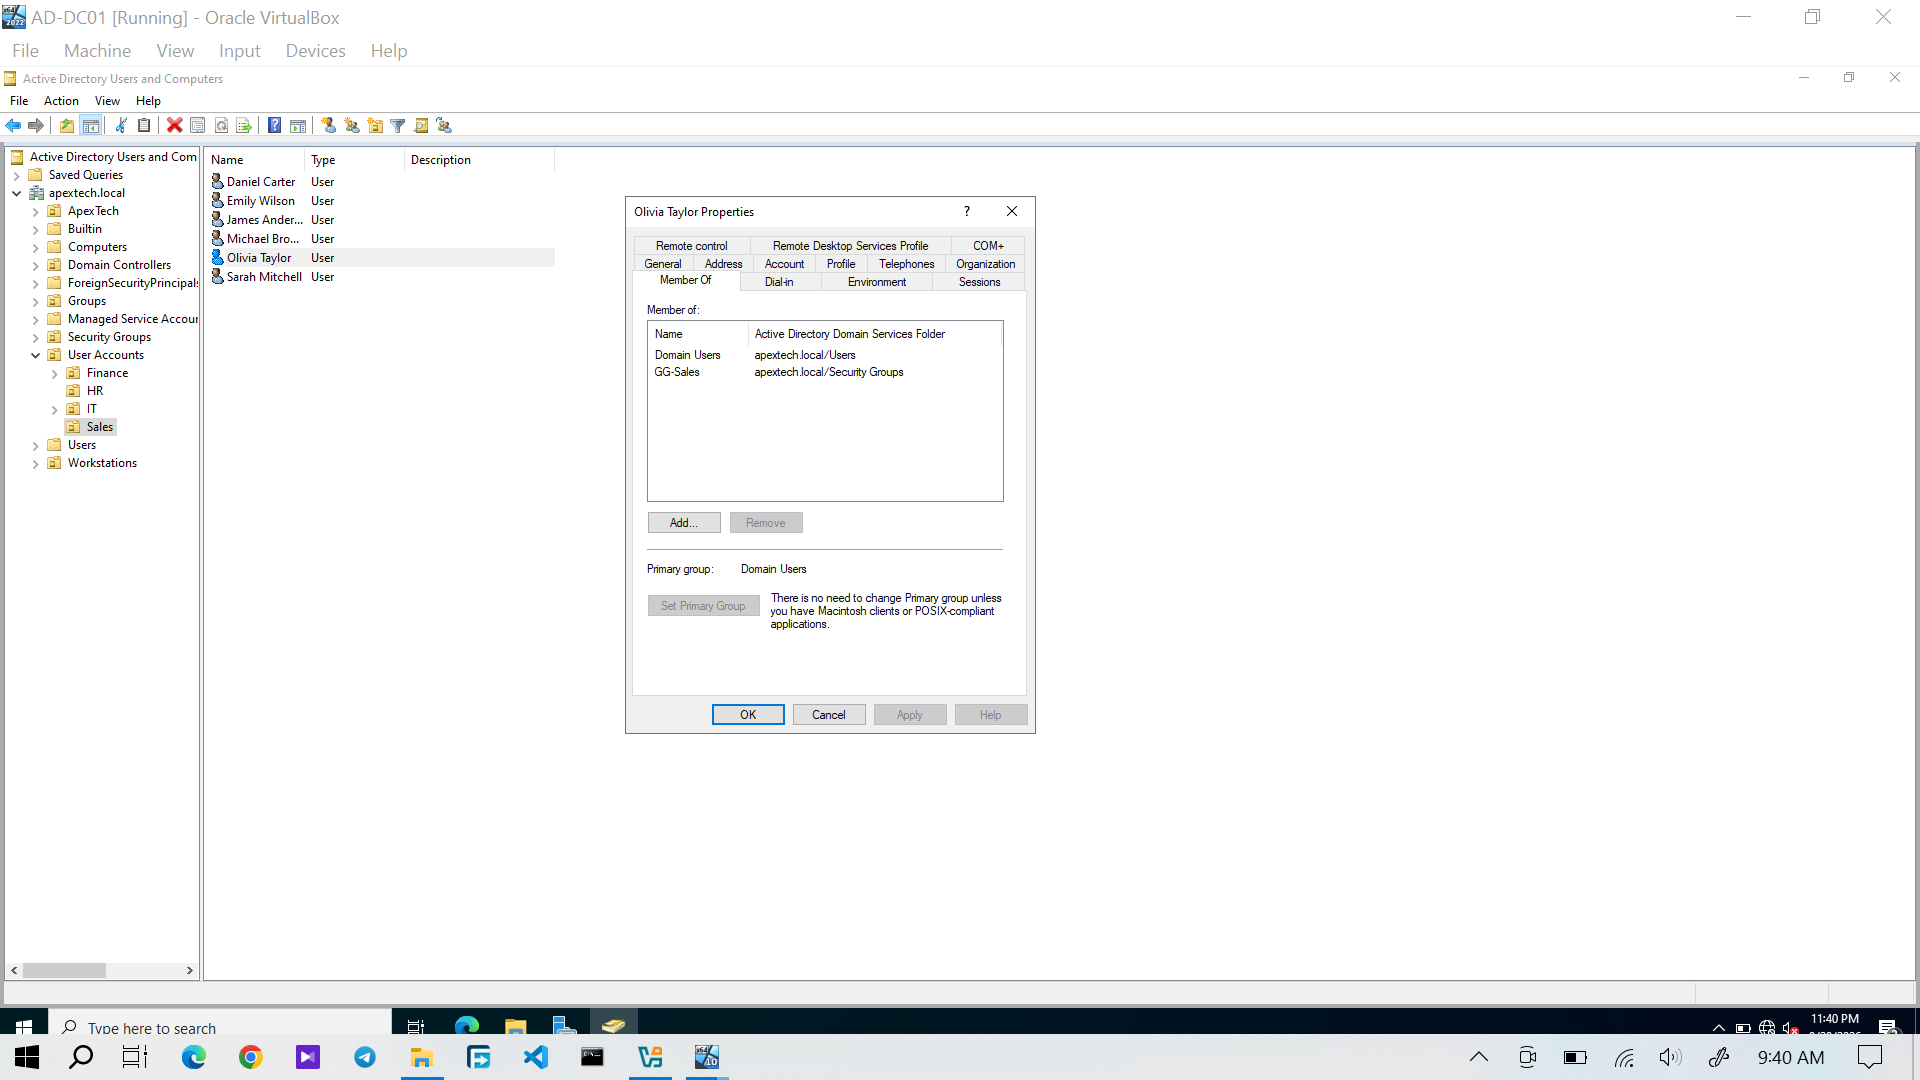
Taylor's Active Directory group membership showing the Sales access assignment.
Taylor was associated with the Sales access model rather than the Finance security group.
This established that the Finance access denial was related to authorization, not a problem with Taylor's account or Windows authentication.
Reviewing Finance Permissions
The Finance resource was then checked to confirm which security group controlled access.
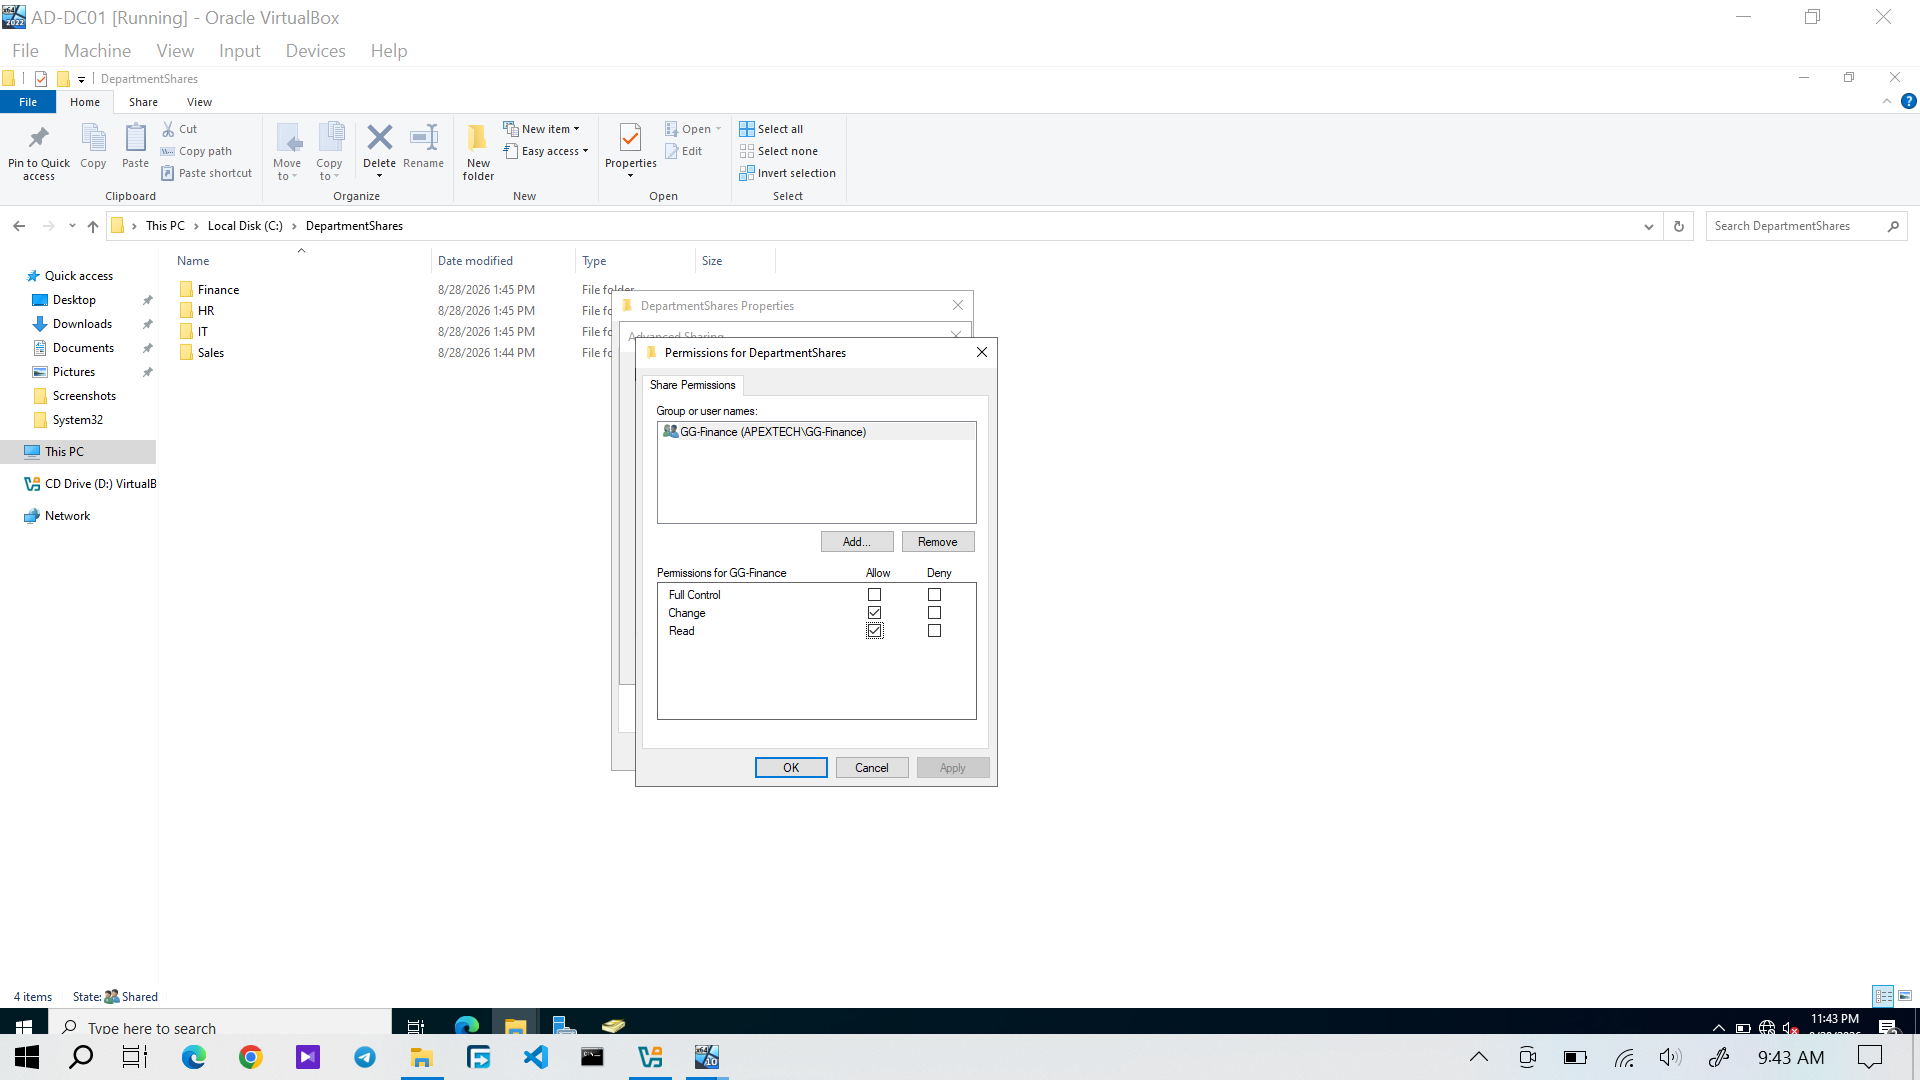
Finance resource permissions showing access controlled through the "GG-Finance" security group.
Taylor was not a member of "GG-Finance".
Access Decision
I did not add Taylor to "GG-Finance" or modify the Finance share permissions.
Instead, the existing access model was preserved:
- Taylor retained access to authorized Sales resources.
- Finance access remained restricted.
- No direct user permissions were added.
- No existing share permissions were changed.
This is an important distinction in IT Support: a user's request for access does not automatically mean the access should be granted.
Verification
To confirm that Taylor's account was functioning normally, access to the authorized Sales resource was tested.
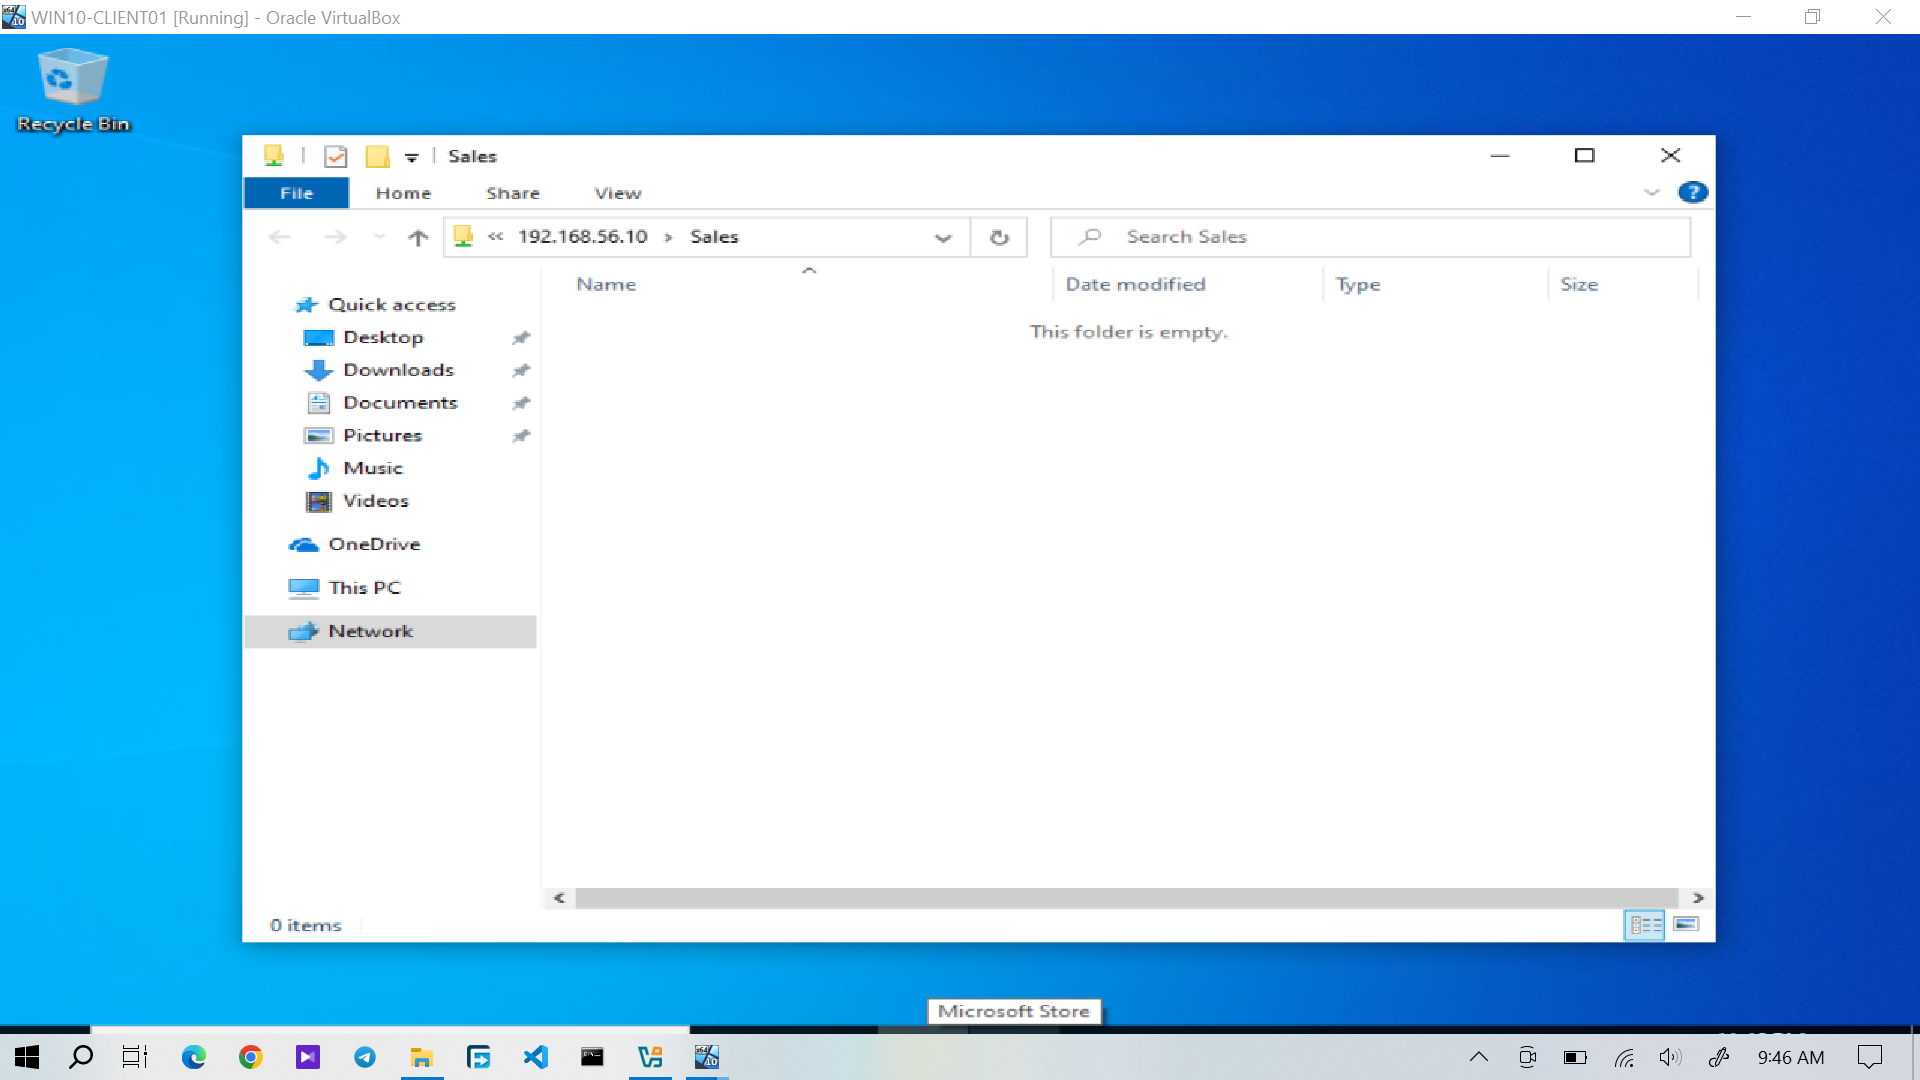
Taylor successfully accessing the authorized Sales resource.
Service Desk Resolution After completing the authorization review, I documented the decision in osTicket and informed Taylor that Finance access could not be granted under the current authorization model.
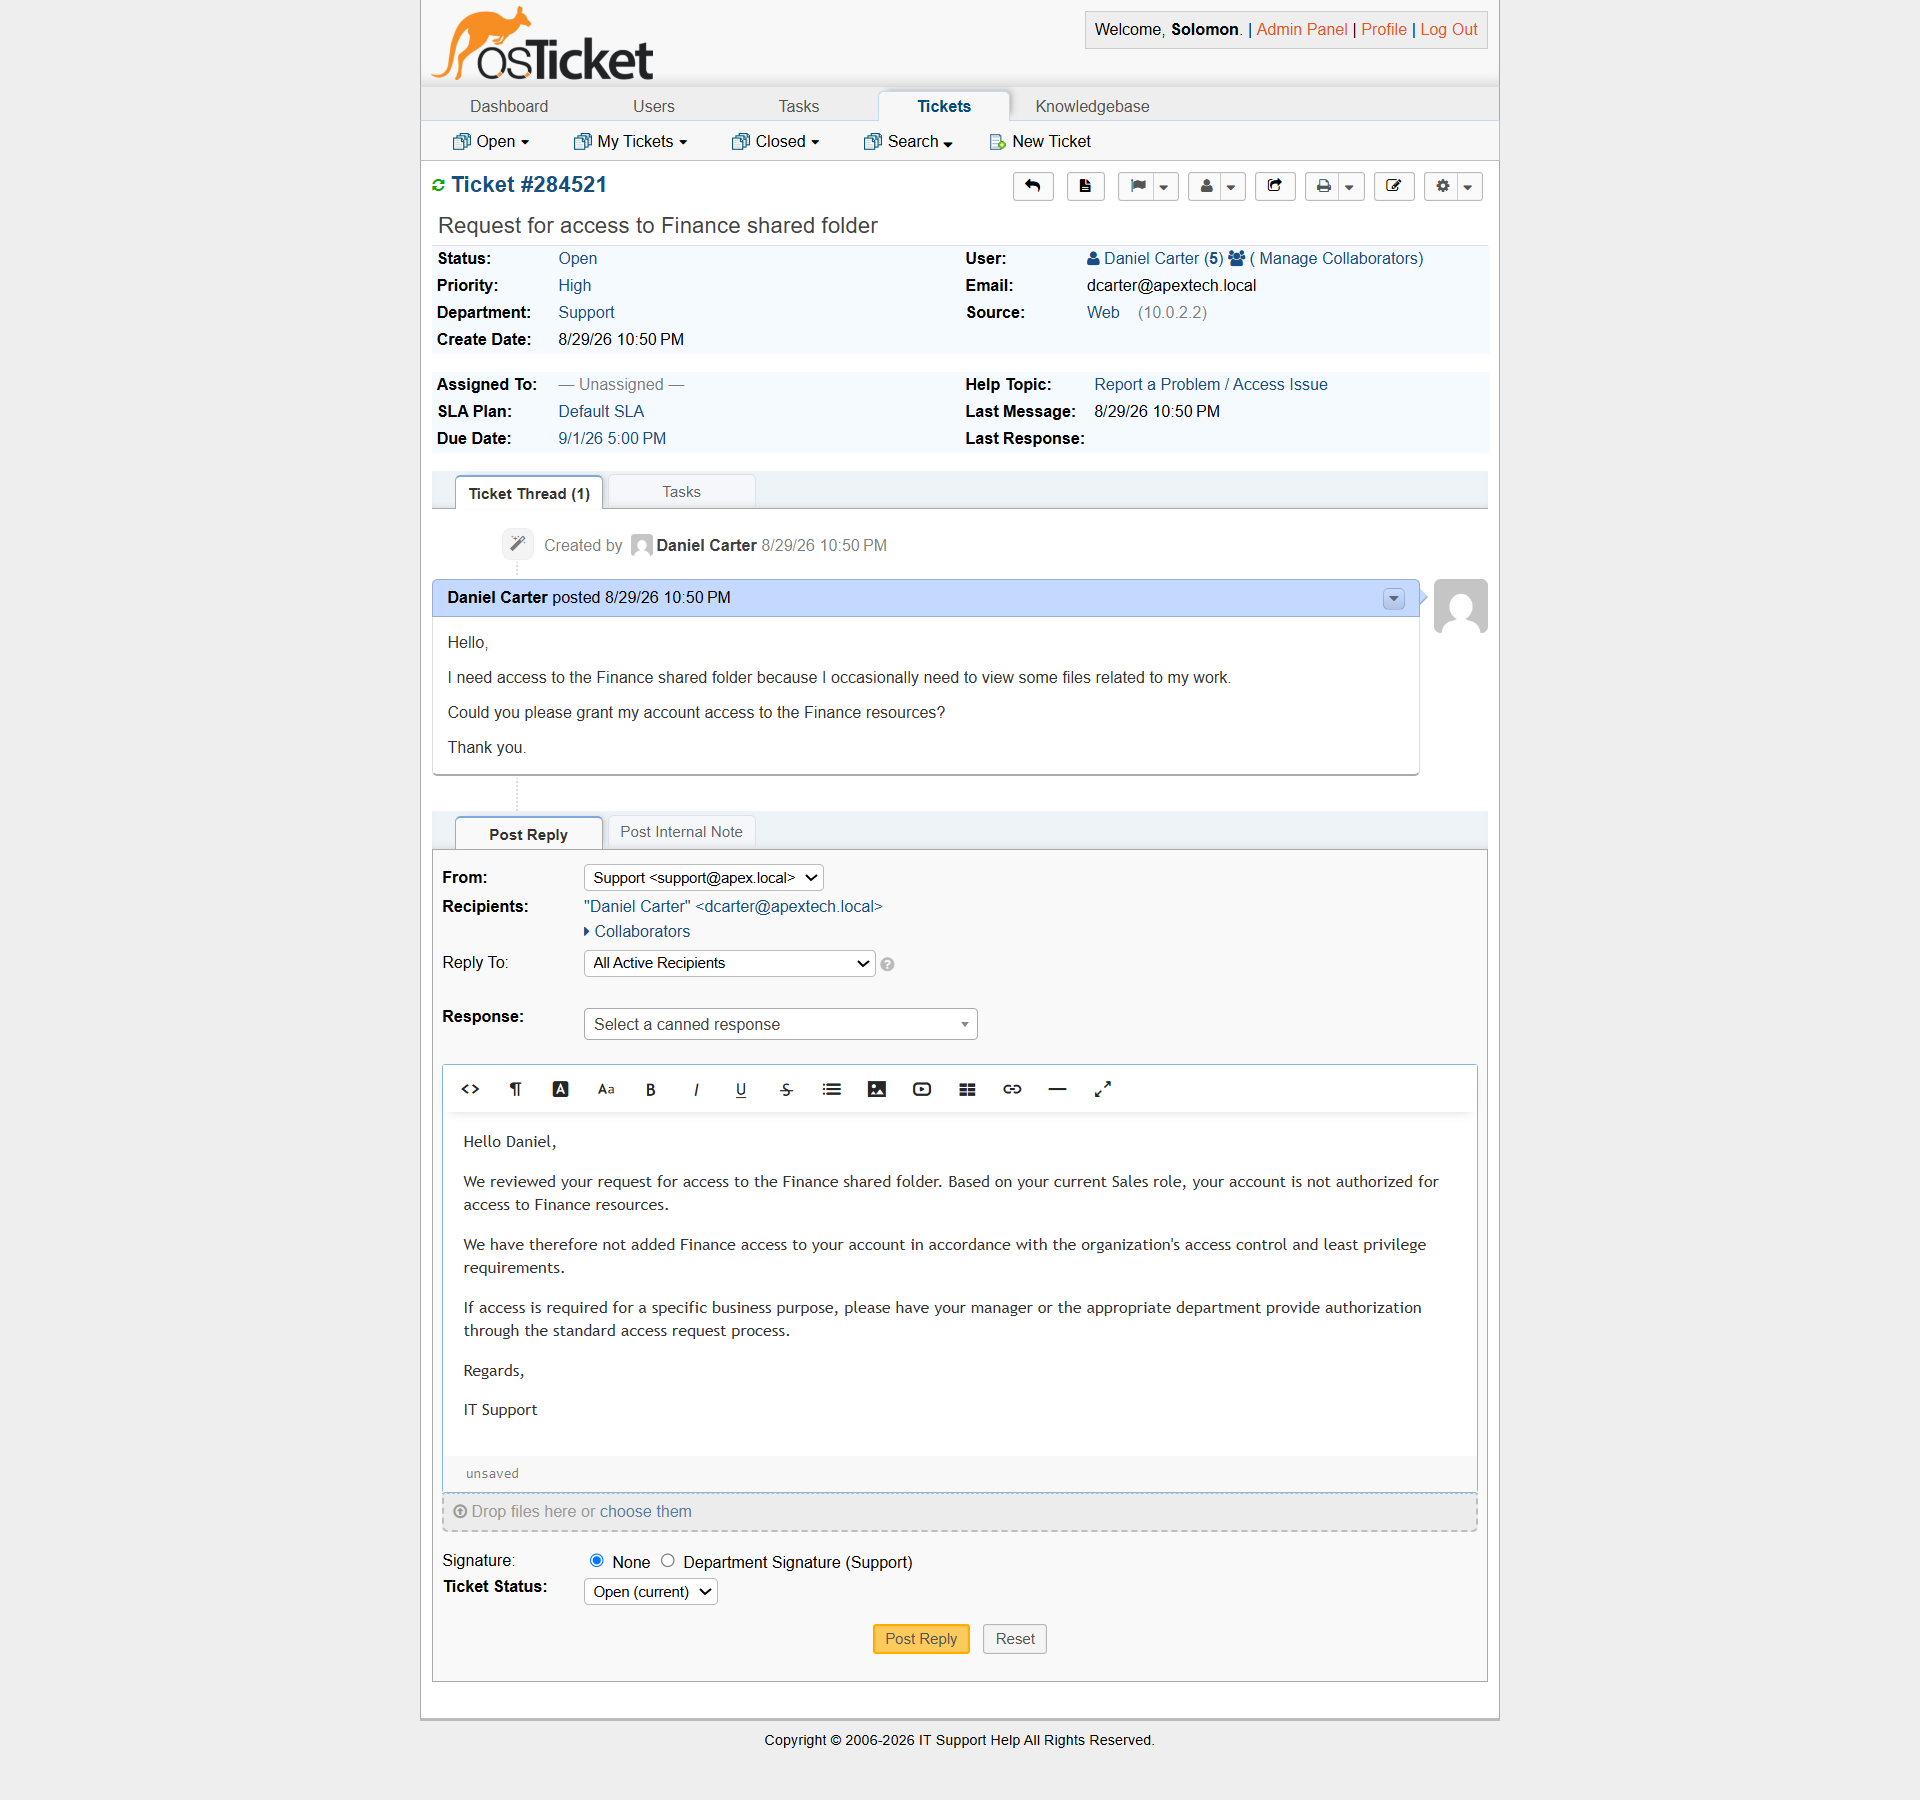
Taylor's Finance access request showing the completed resolution and ticket closure in osTicket.
The ticket was closed after the request had been reviewed, the authorization decision documented, and Taylor's existing authorized access verified.