Department Shares & Permissions
After the Active Directory users and security groups were created, departmental file resources were configured to demonstrate access control in the Windows environment.
Four departmental areas were established:
- IT
- Finance
- HR
- Sales
Access to these resources was managed through Active Directory security groups together with Windows file-sharing and NTFS permissions.
Department File Structure
Department specific folders were created to represent shared organizational resources.
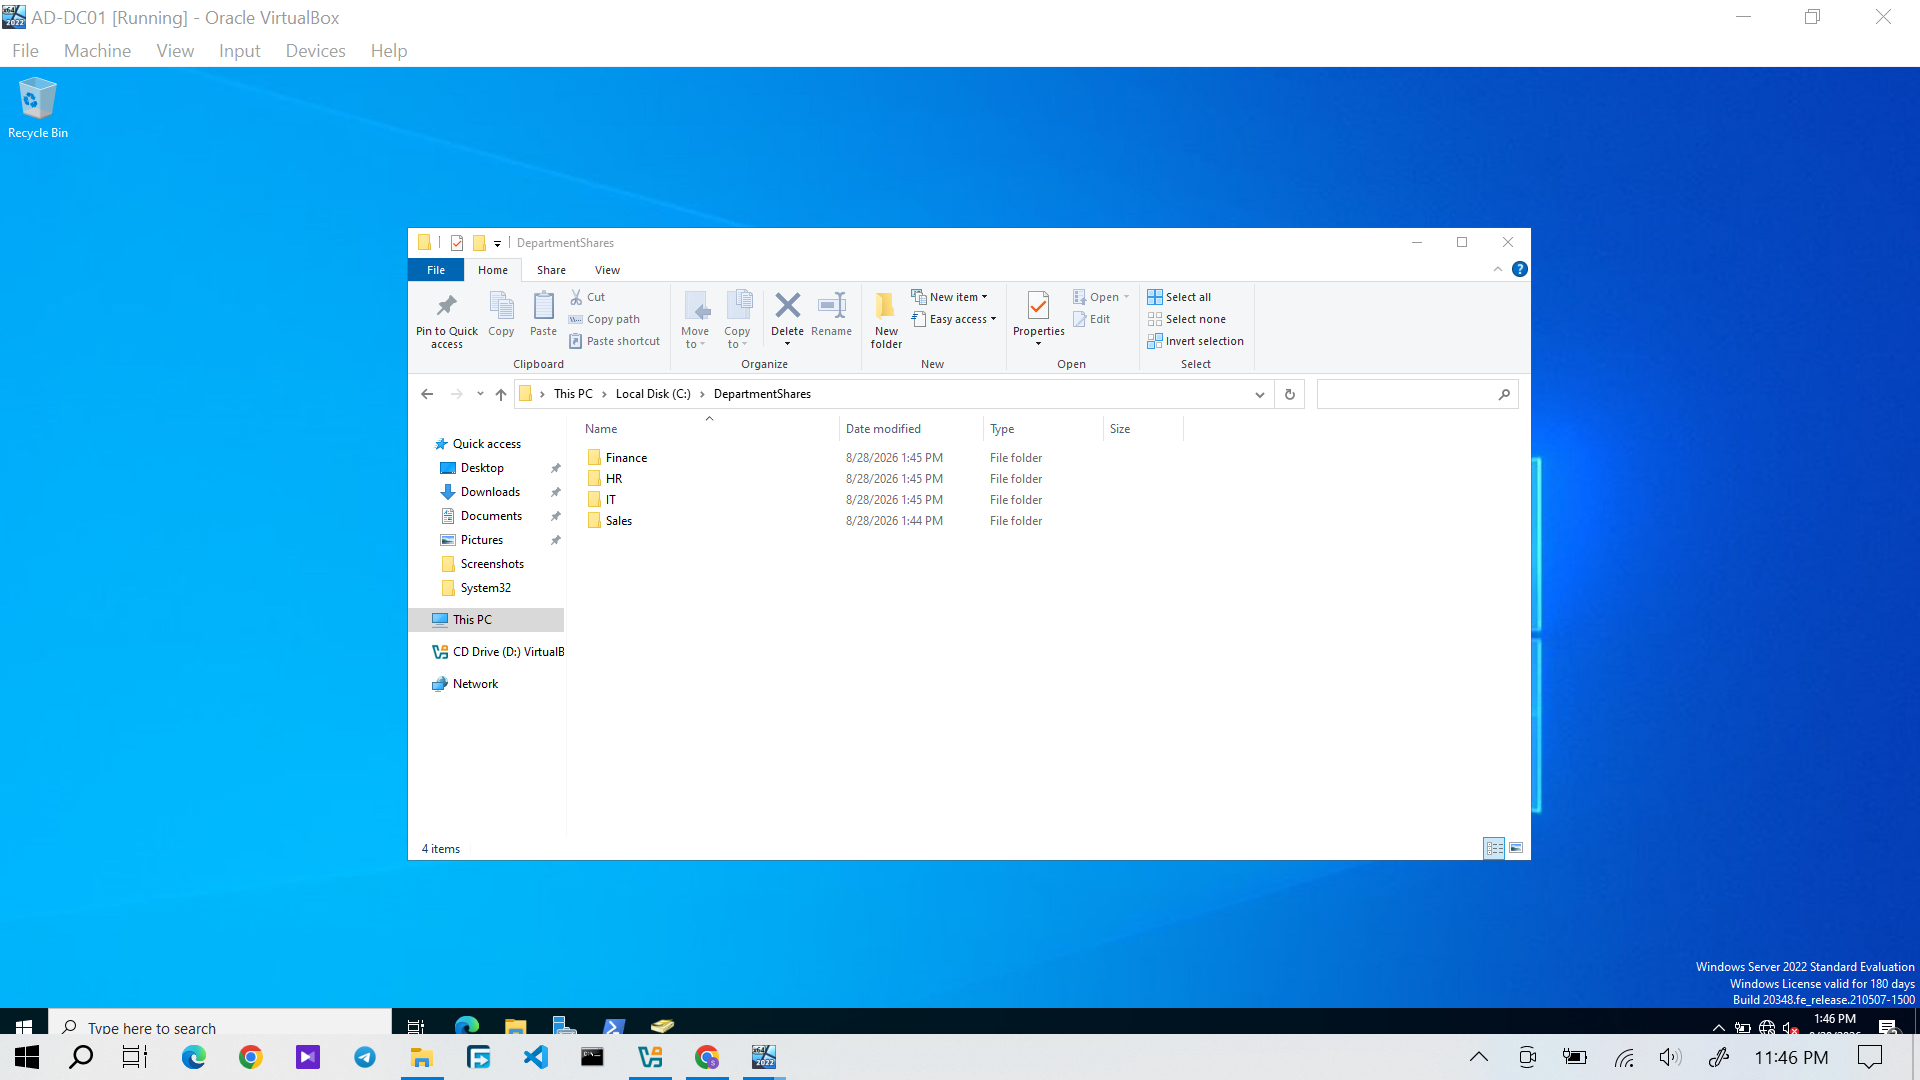
Figure 1: Department folders created for the laboratory environment.
These folders provided the resources used for subsequent access-control testing.
The basic permission relationship was:
Using security groups allows access to be managed centrally rather than assigning permissions separately to every user.Sales Shared Folder
The Sales folder was configured as a shared network resource.
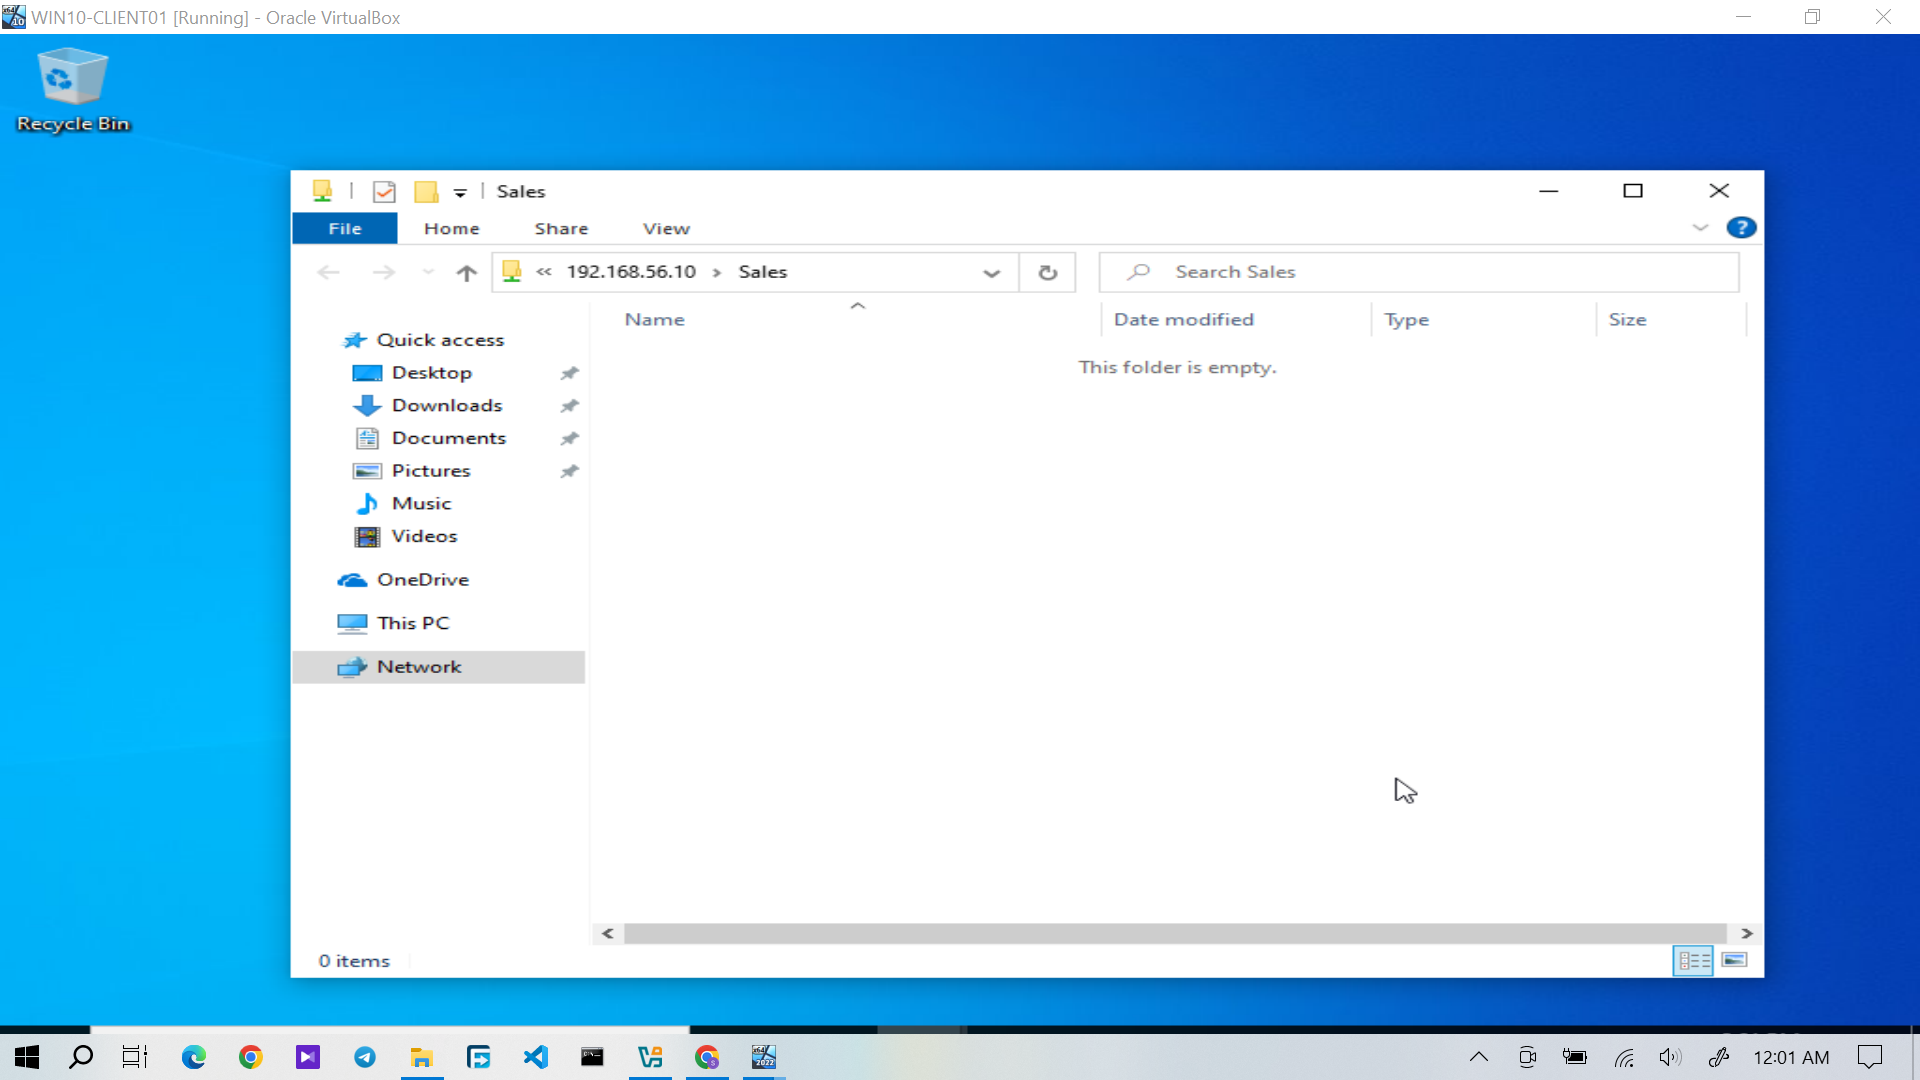
Figure 2: Sales departmental folder configured as a shared resource.
Testing Department Access
The permission configuration was tested using users from different departments.
An unauthorized access attempt was deliberately performed to confirm that departmental resources were not available to every domain user.
"Access denied to HR folder" (assets/images/27%20windows%20cant%20access%20HR%20folder.png)
Figure 3: Windows denying access to a departmental resource.
The access-denied result confirmed that the configured permissions were enforcing the intended access restrictions.
Daniel Carter — Sales Access
Daniel Carter was used to verify authorized access to the Sales resource.
His Active Directory group membership was checked before testing the share.
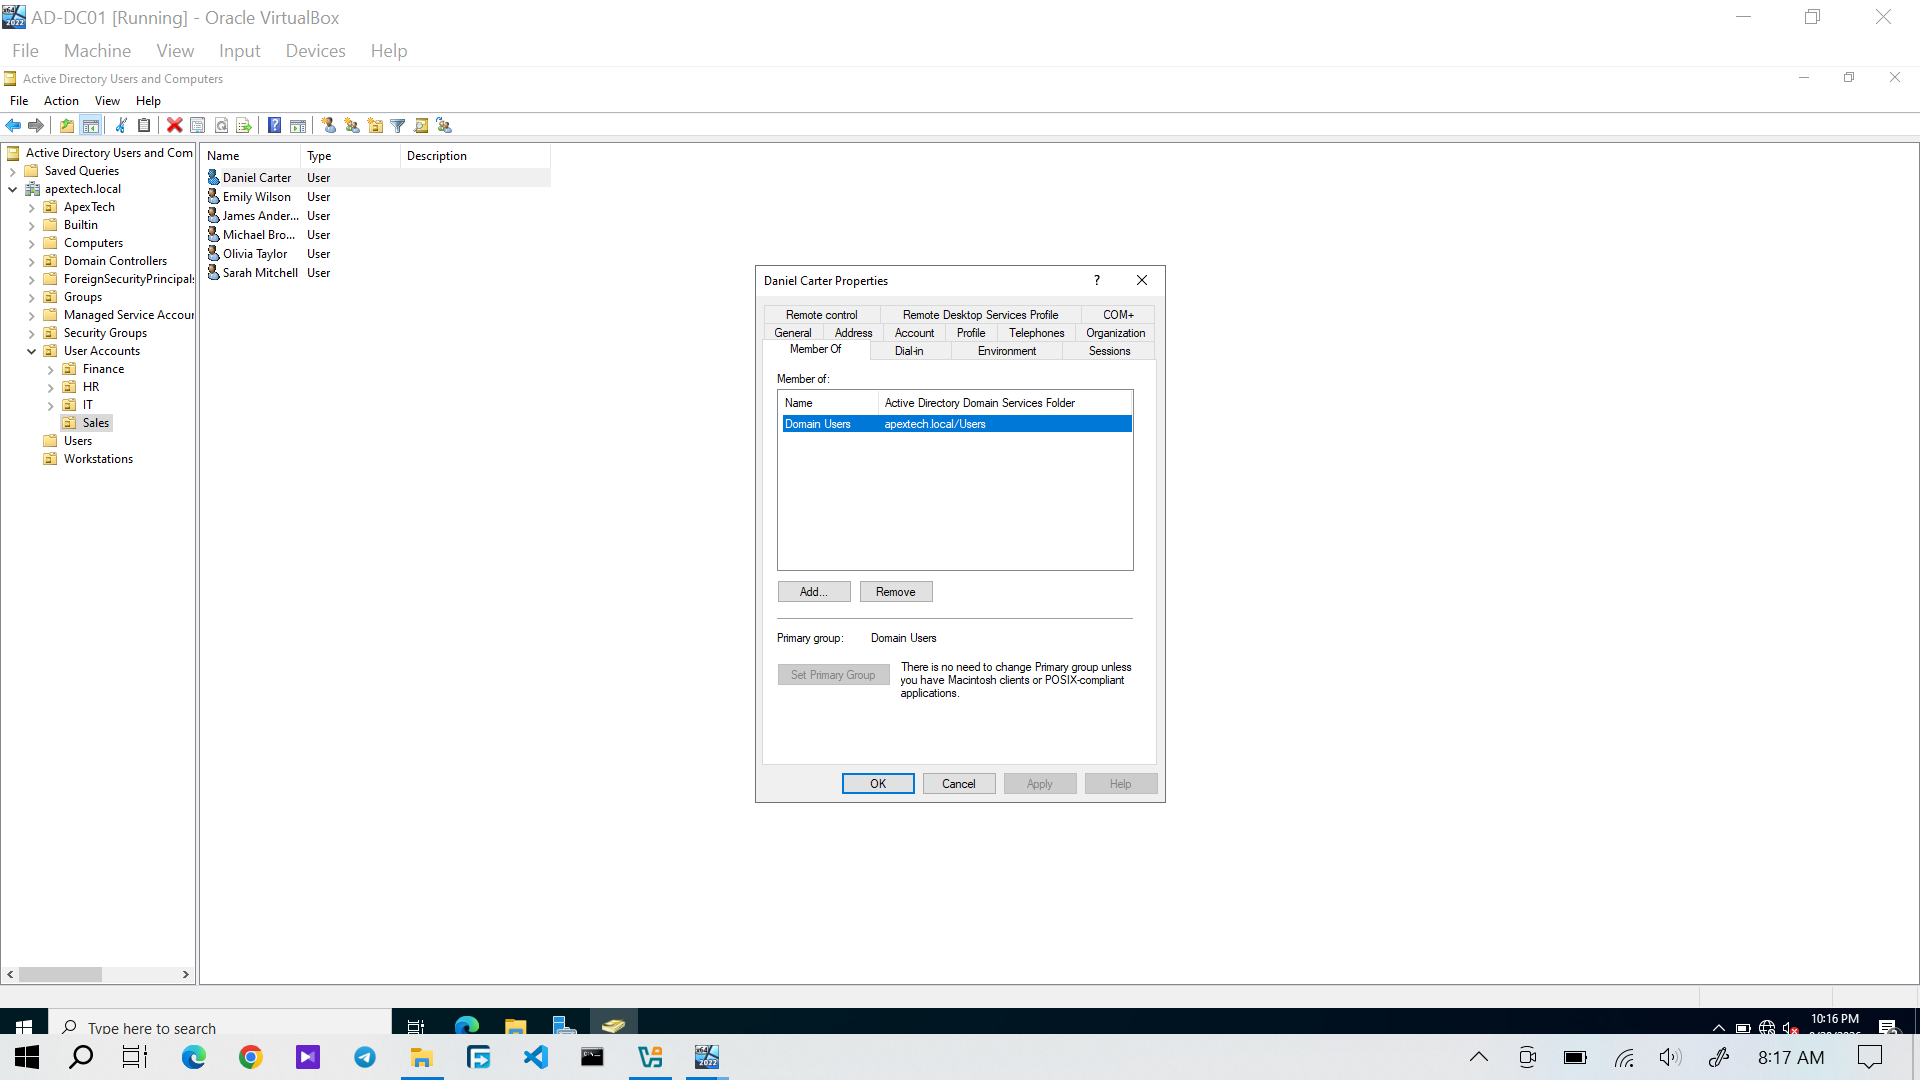
Figure 4: Daniel Carter's Active Directory group membership.
His membership in the Sales security group provided the authorization required to access the Sales resource.
Rachel Adams — HR Access
Rachel Adams was used to verify access to the HR resource.
Her membership in the HR security group was confirmed before testing access.
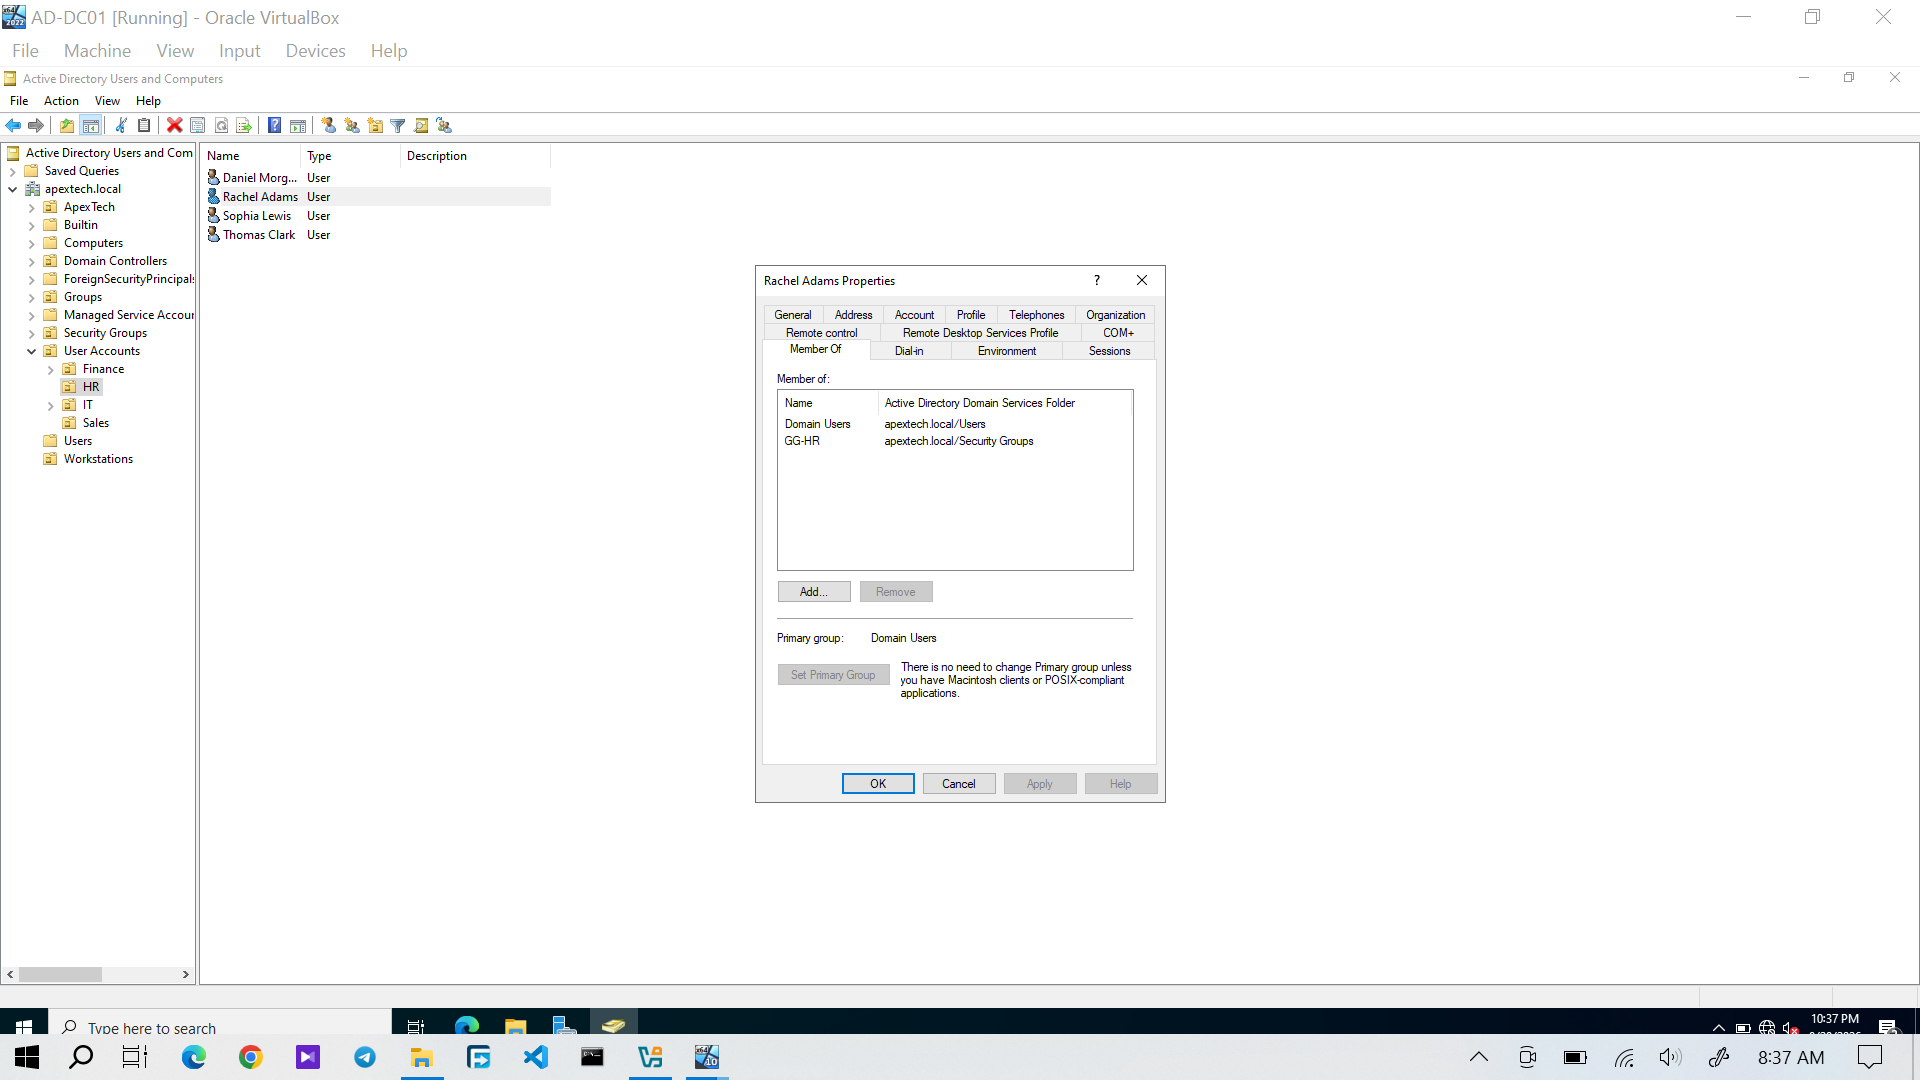
Figure 5: Rachel Adams' HR security-group membership.
After confirming her group membership, access to the HR shared resource was tested.
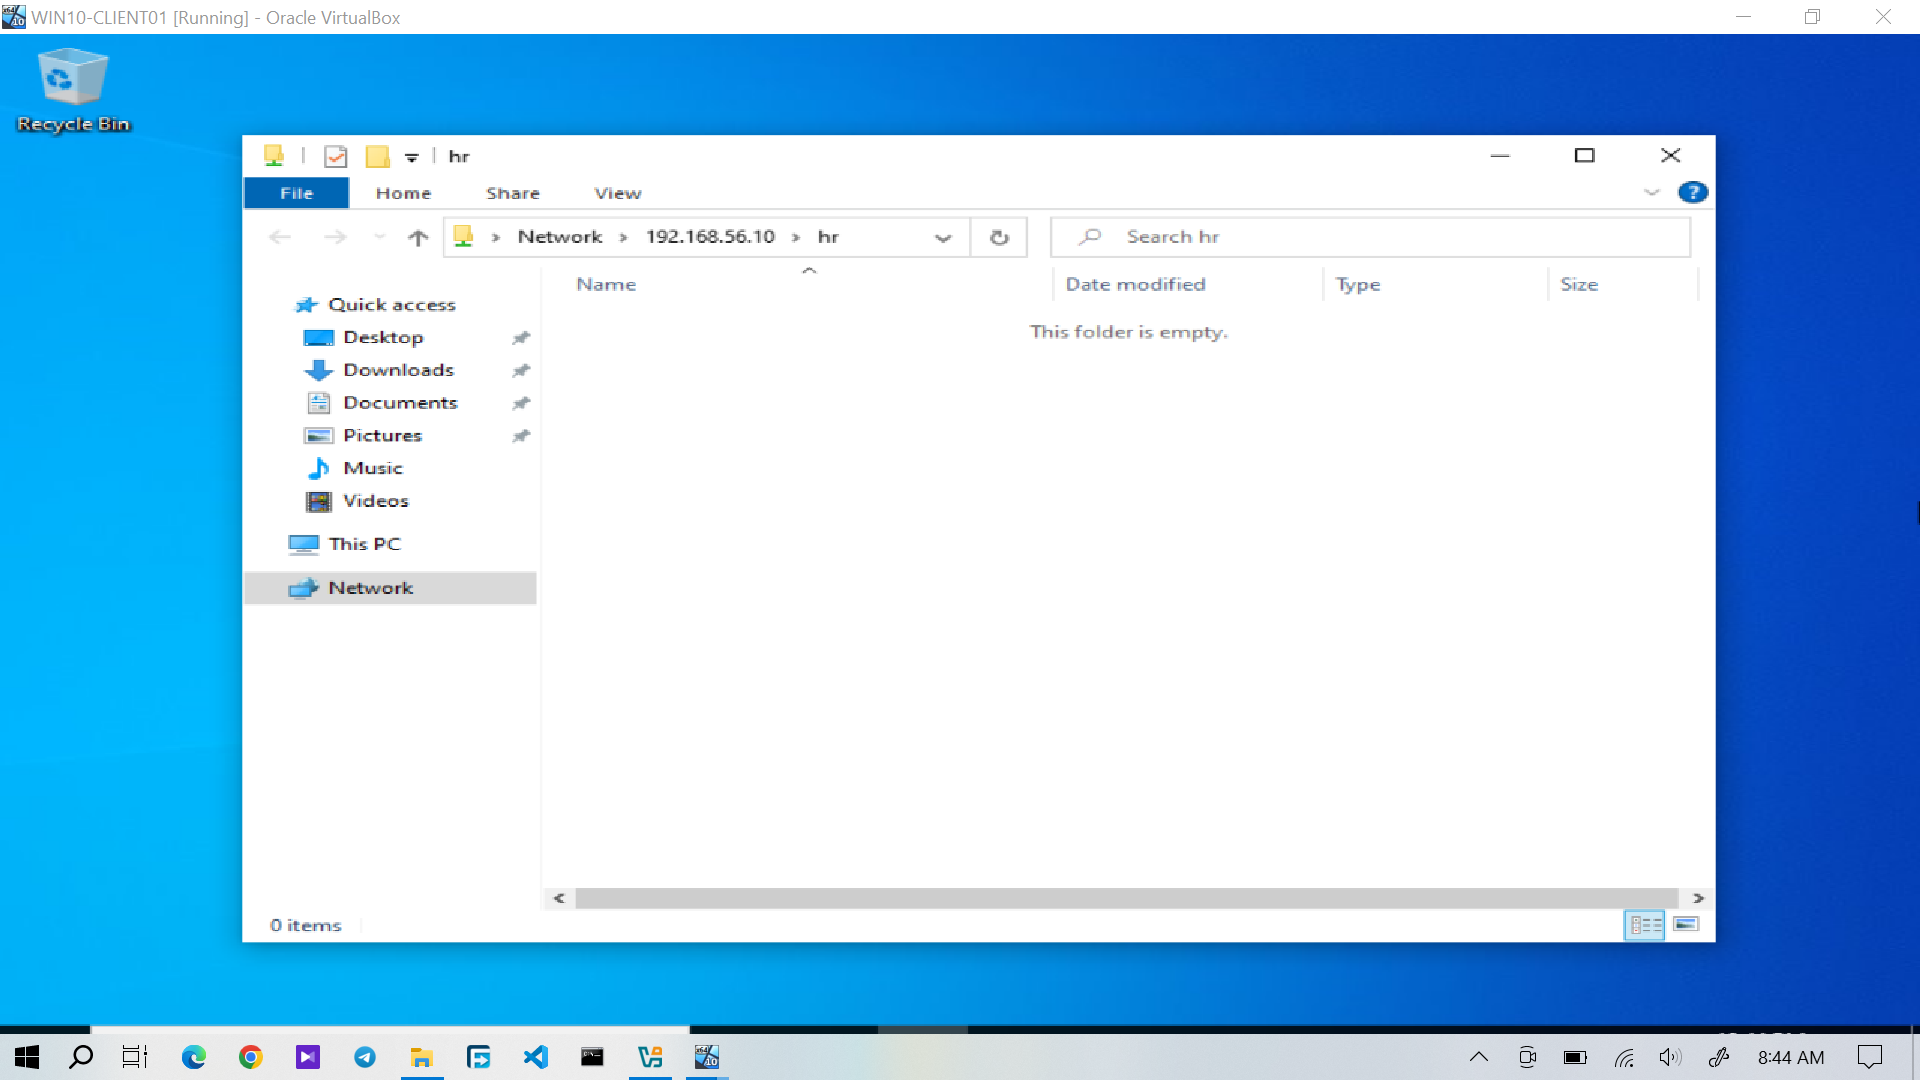
Figure 6: Rachel Adams successfully accessing the HR shared resource.
Testing Unauthorized Finance Access
A negative access test was also performed using Rachel Adams against the Finance resource.
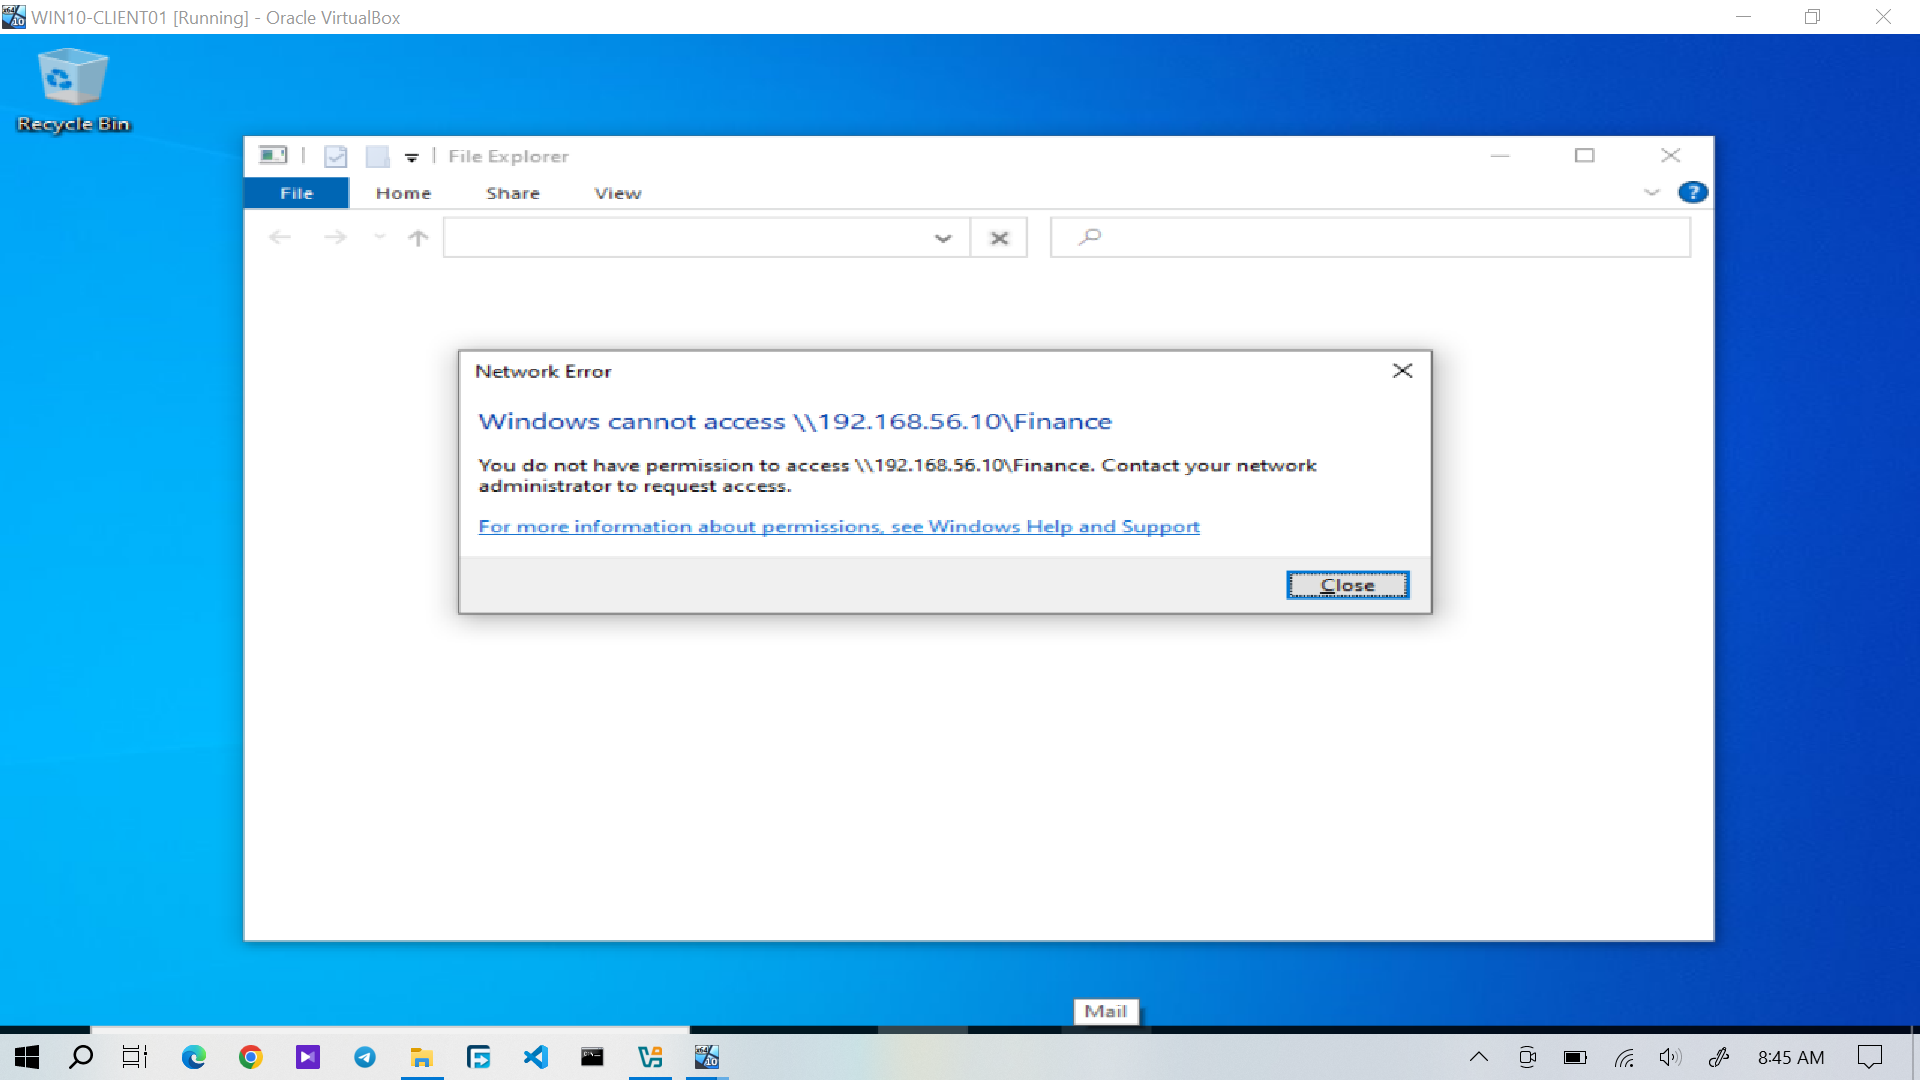
Figure 7: Rachel Adams receiving an access-denied result when attempting to access the Finance resource.
This confirmed that the permissions were restricting access according to the user's assigned authorization.
Result
The lab now contains a working departmental file sharing environment with access controlled through security groups and Windows permissions.