Ticket 08 — Employee Offboarding
Ticket Summary
Thomas was scheduled to leave the organization and required his Active Directory account to be deprovisioned.
The objective was to prevent further domain authentication while retaining the account for administrative purposes. Instead of deleting the account, I disabled it and moved it to the designated Disabled Users organizational unit.
User Request
Thomas's offboarding request was submitted through the service desk.
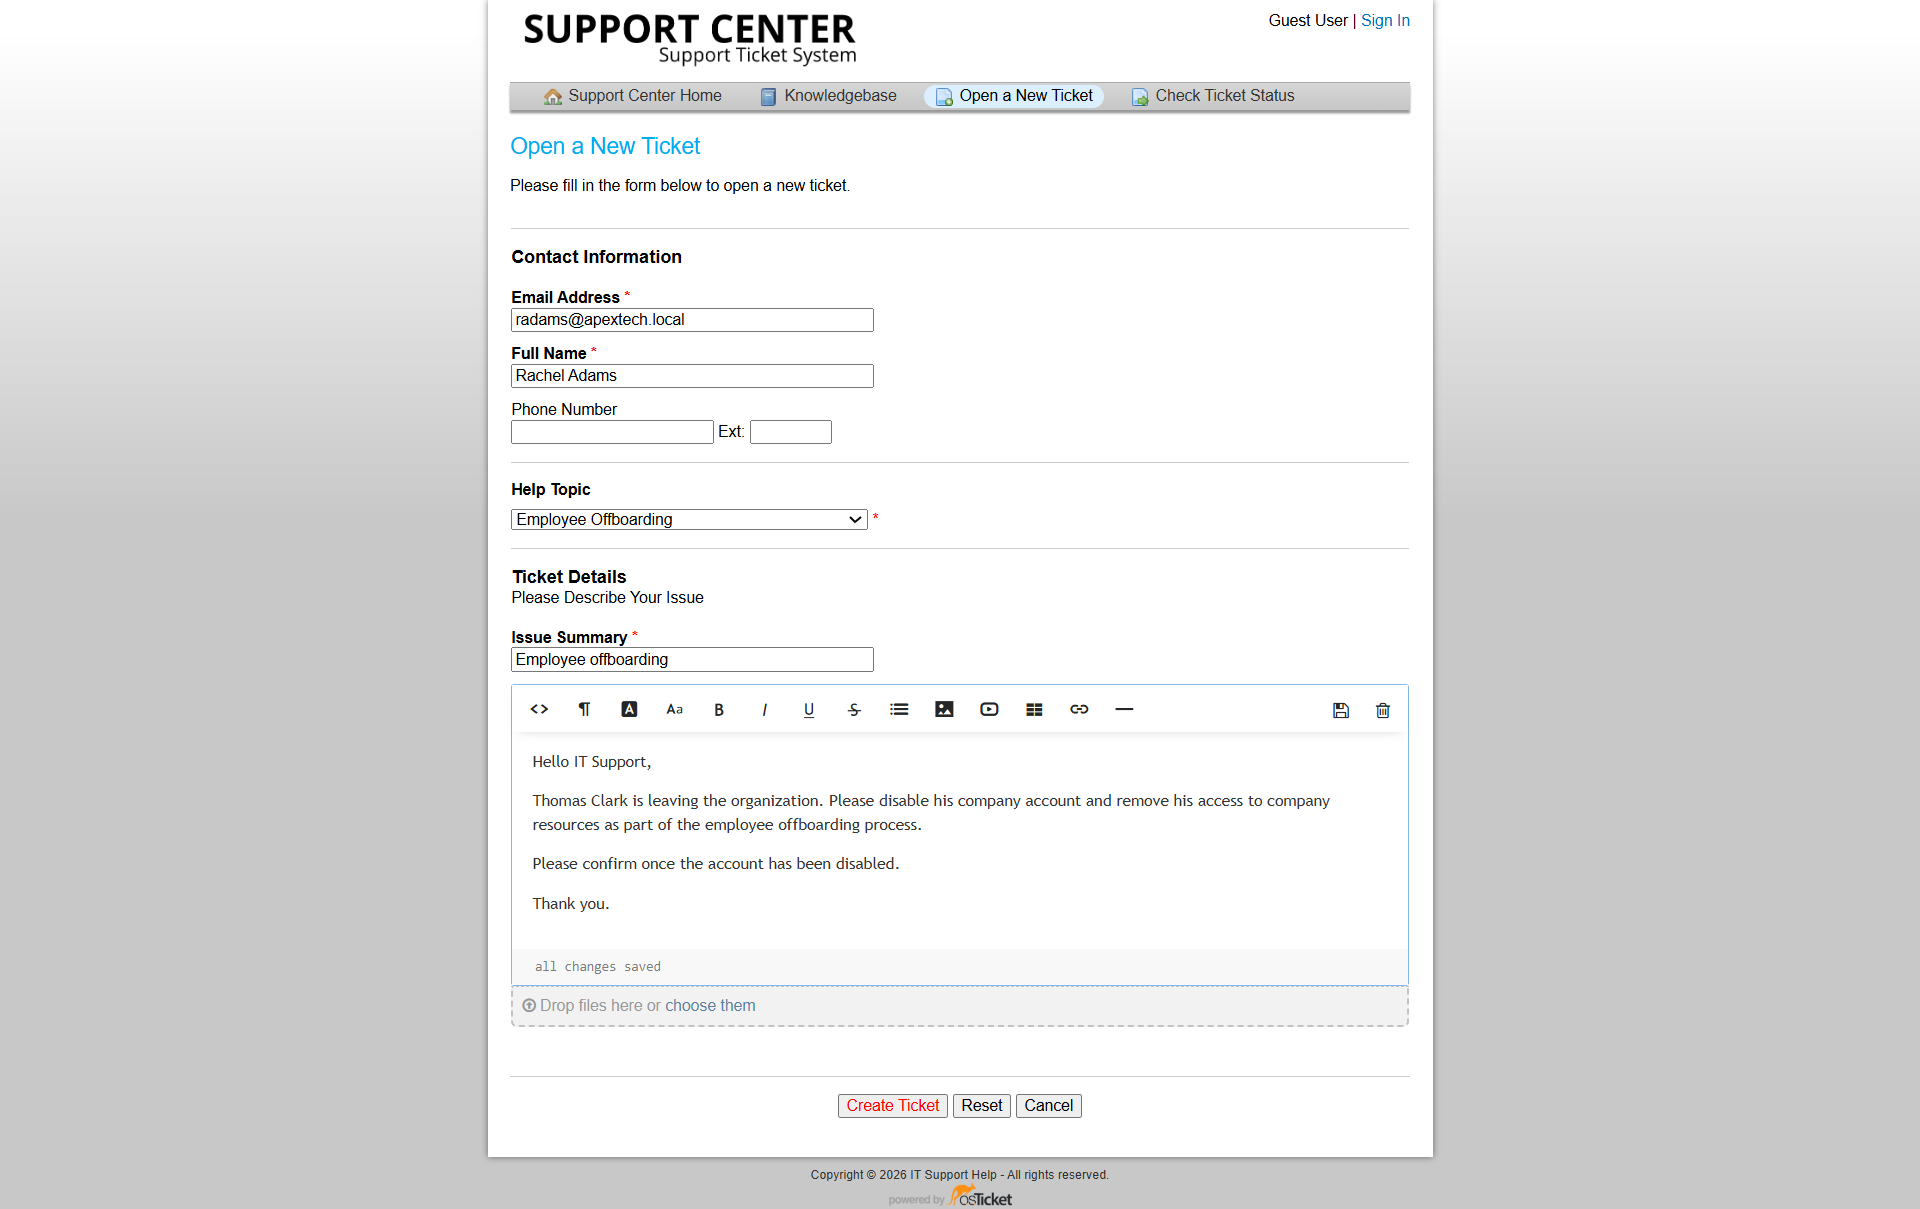
Thomas's employee-offboarding request submitted through osTicket.
Initial Assessment
I first identified Thomas's Active Directory account and confirmed its current state.
The required actions were:
- Disable the domain account.
- Verify that authentication was blocked.
- Move the disabled account to the Disabled Users OU.
- Document the completed work in the service desk.
Account Before Offboarding
Thomas's account was reviewed before the offboarding action.
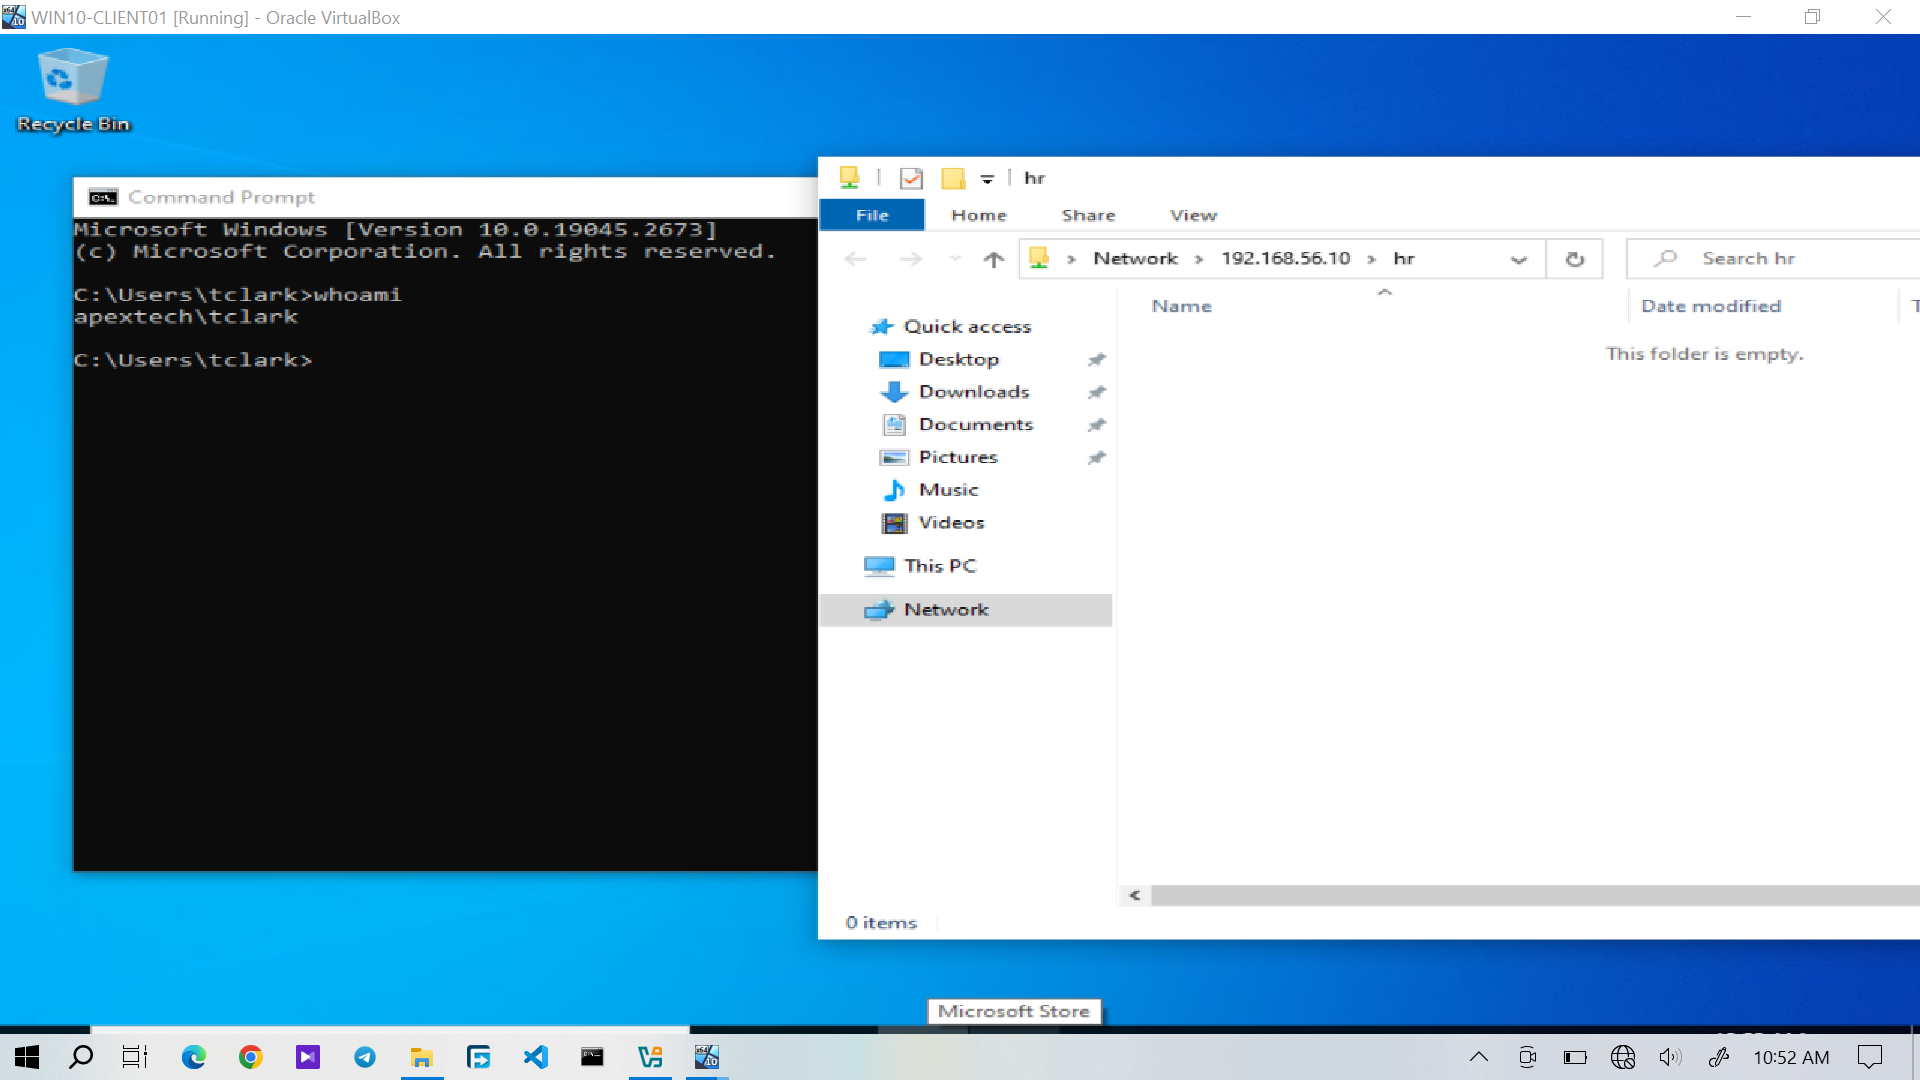
Thomas's Active Directory account before offboarding.
Technical Resolution
I disabled Thomas's Active Directory account.
Disabling the account prevents it from being used for domain authentication while keeping the account object available in Active Directory.
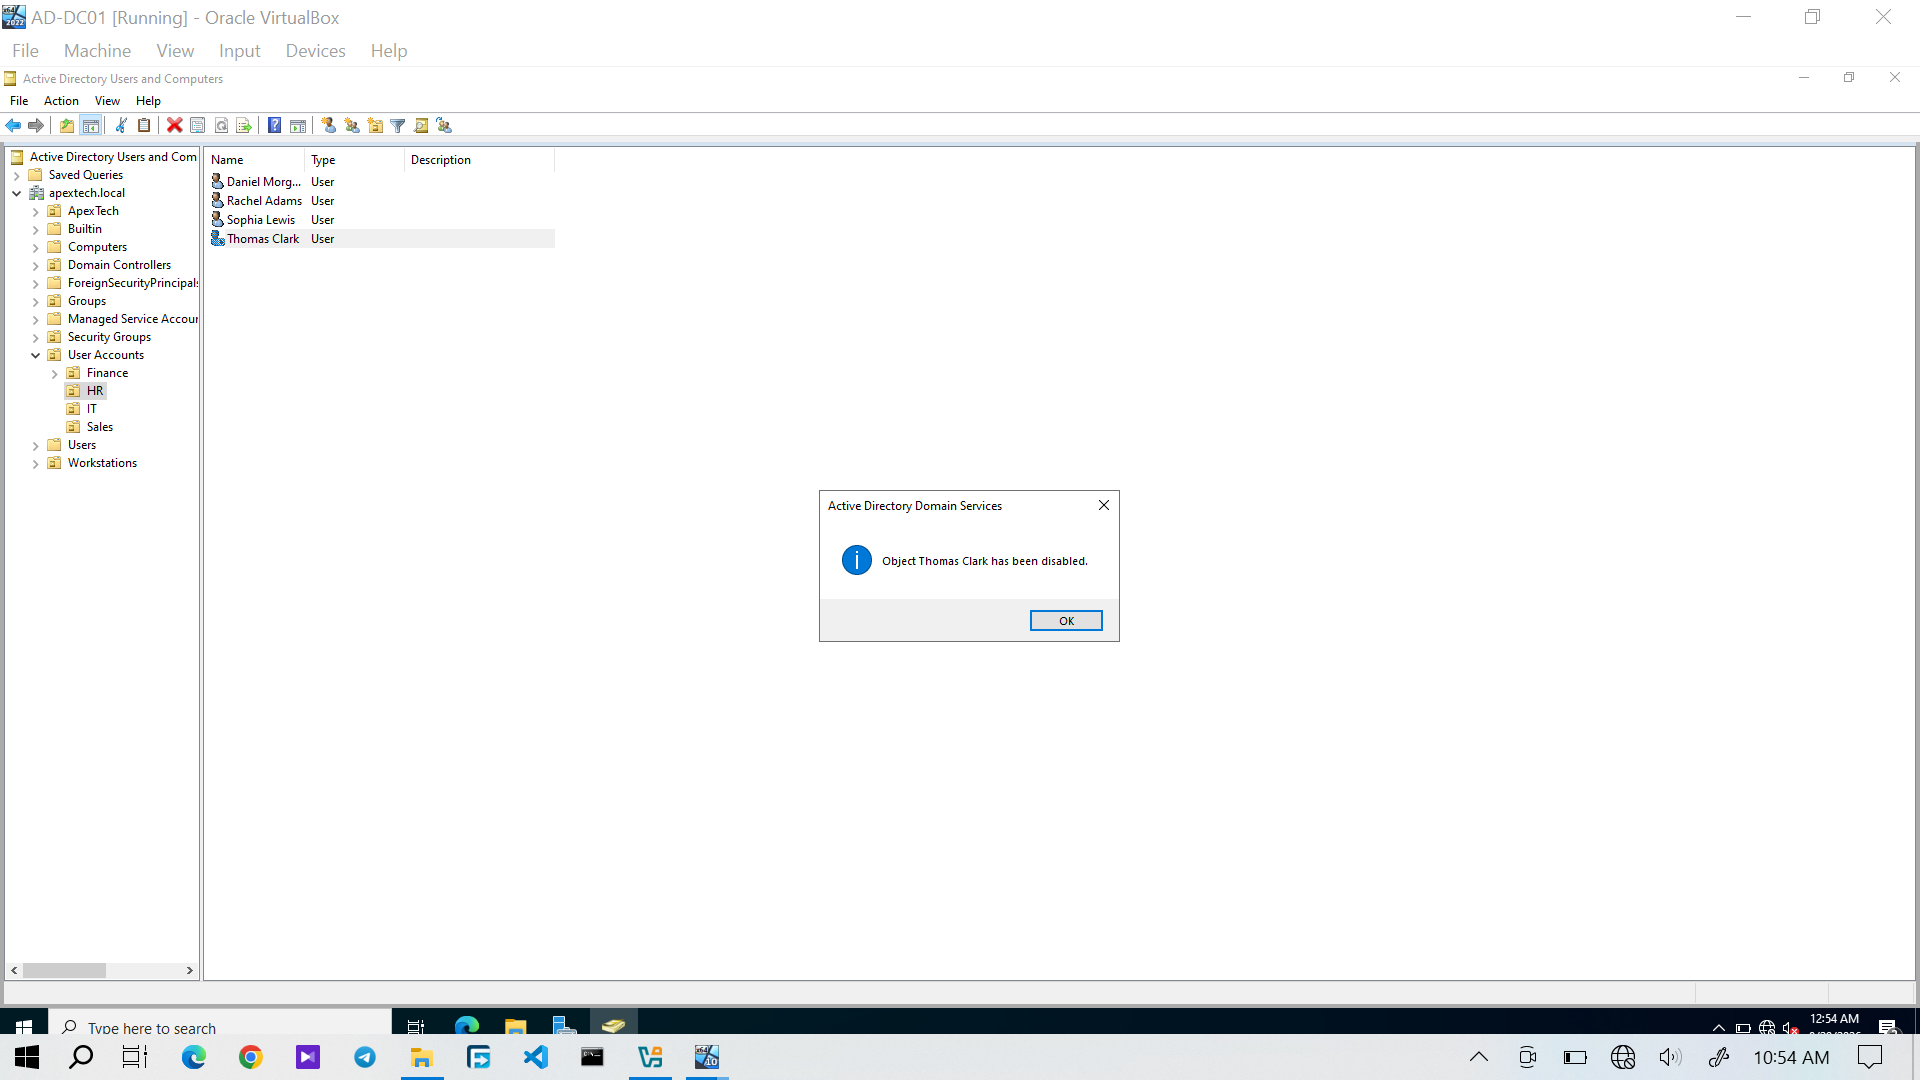
Thomas's Active Directory account after it was disabled.
The resulting state was:
No unnecessary changes were made to the account or the surrounding Active Directory structure.Authentication Verification
I then verified the effect of the account change by attempting to authenticate using Thomas's domain account.
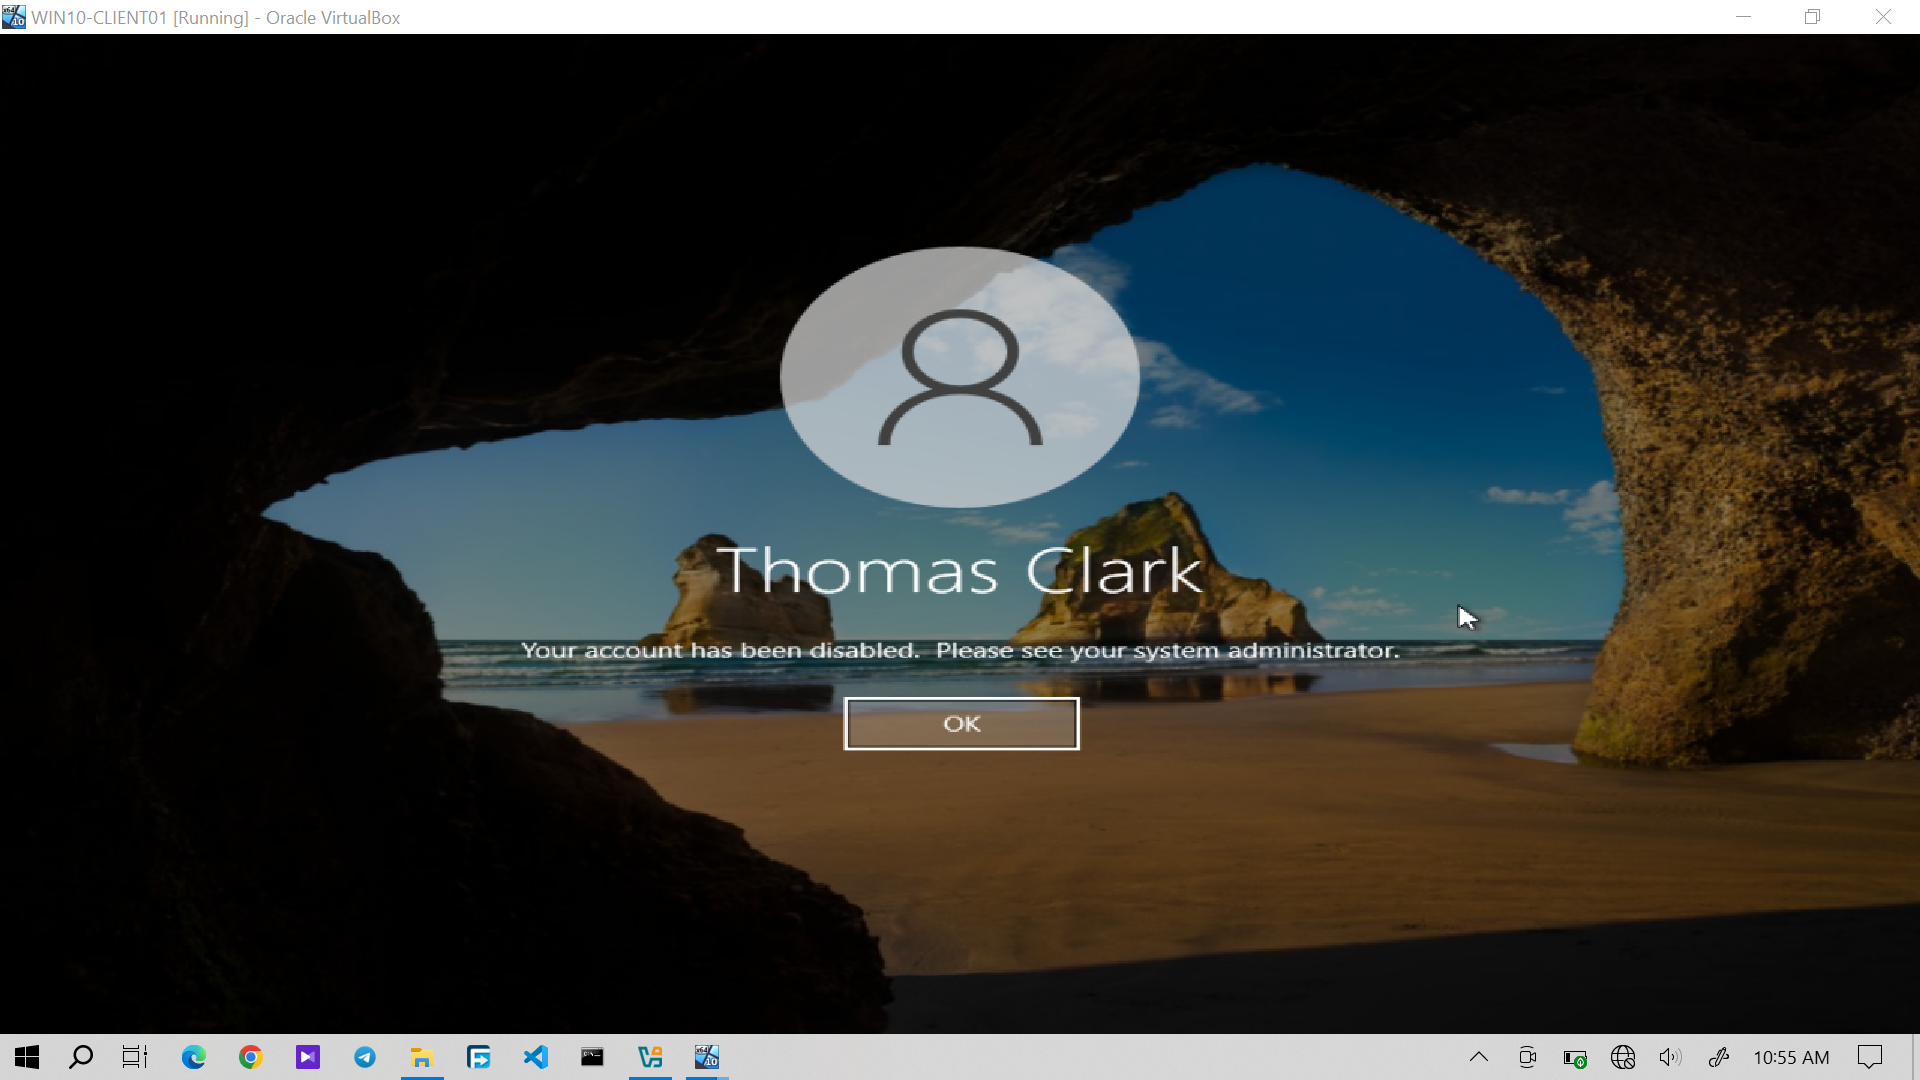
Authentication blocked after Thomas's domain account was disabled.
Disabled Users OU
After confirming that authentication was blocked, Thomas's account was moved into the designated Disabled Users organizational unit.
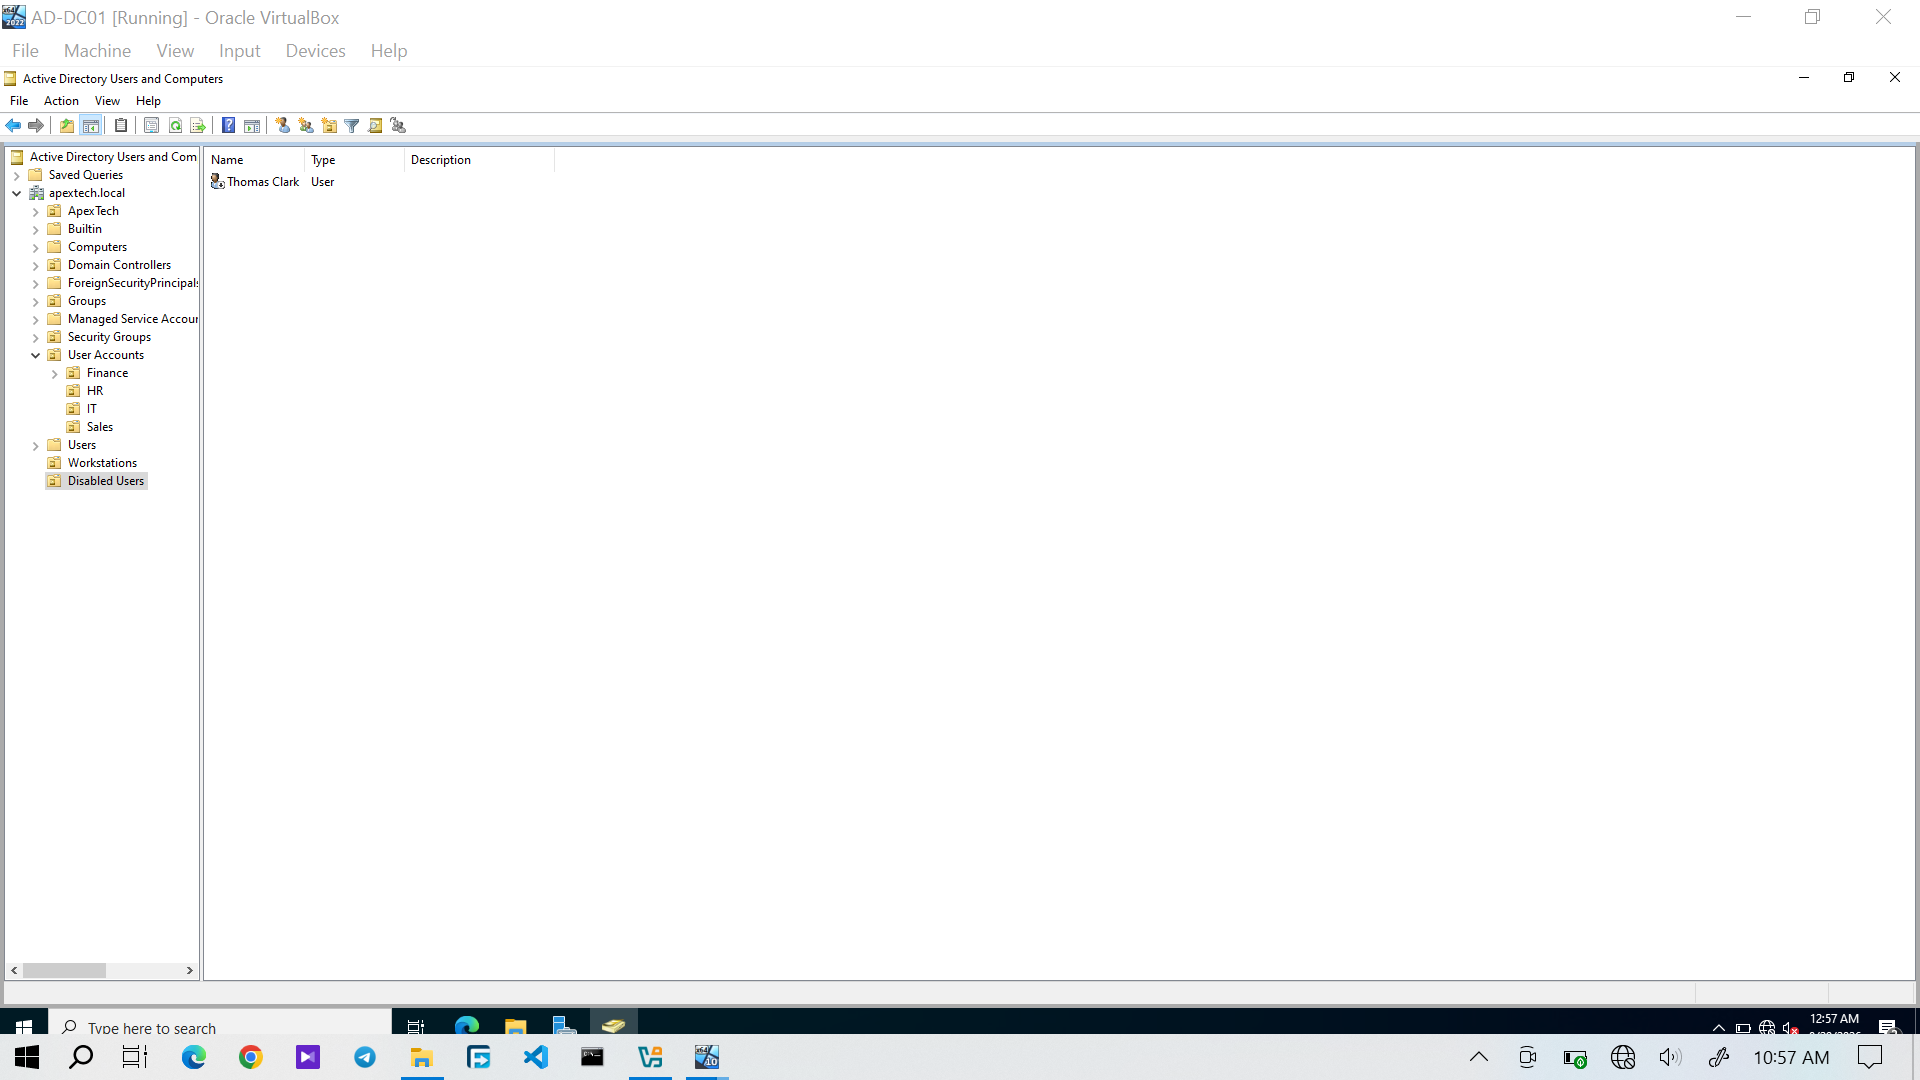
Thomas's disabled account located in the designated Disabled Users OU.
Separating disabled accounts from active users provides a clearer administrative structure and makes account lifecycle management easier.
The completed process was:
Active User
     │
     ▼
Employee Offboarding
     │
     ▼
Account Disabled
     │
     ▼
Authentication Blocked
     │
     ▼
Disabled Users OU
Verification
The offboarding action was verified at two levels.
Active Directory verification
- Thomas's account was confirmed as disabled.
- The account was located in the Disabled Users OU.
Service Desk Resolution
After the Active Directory changes and authentication verification were completed, I documented the outcome in osTicket.
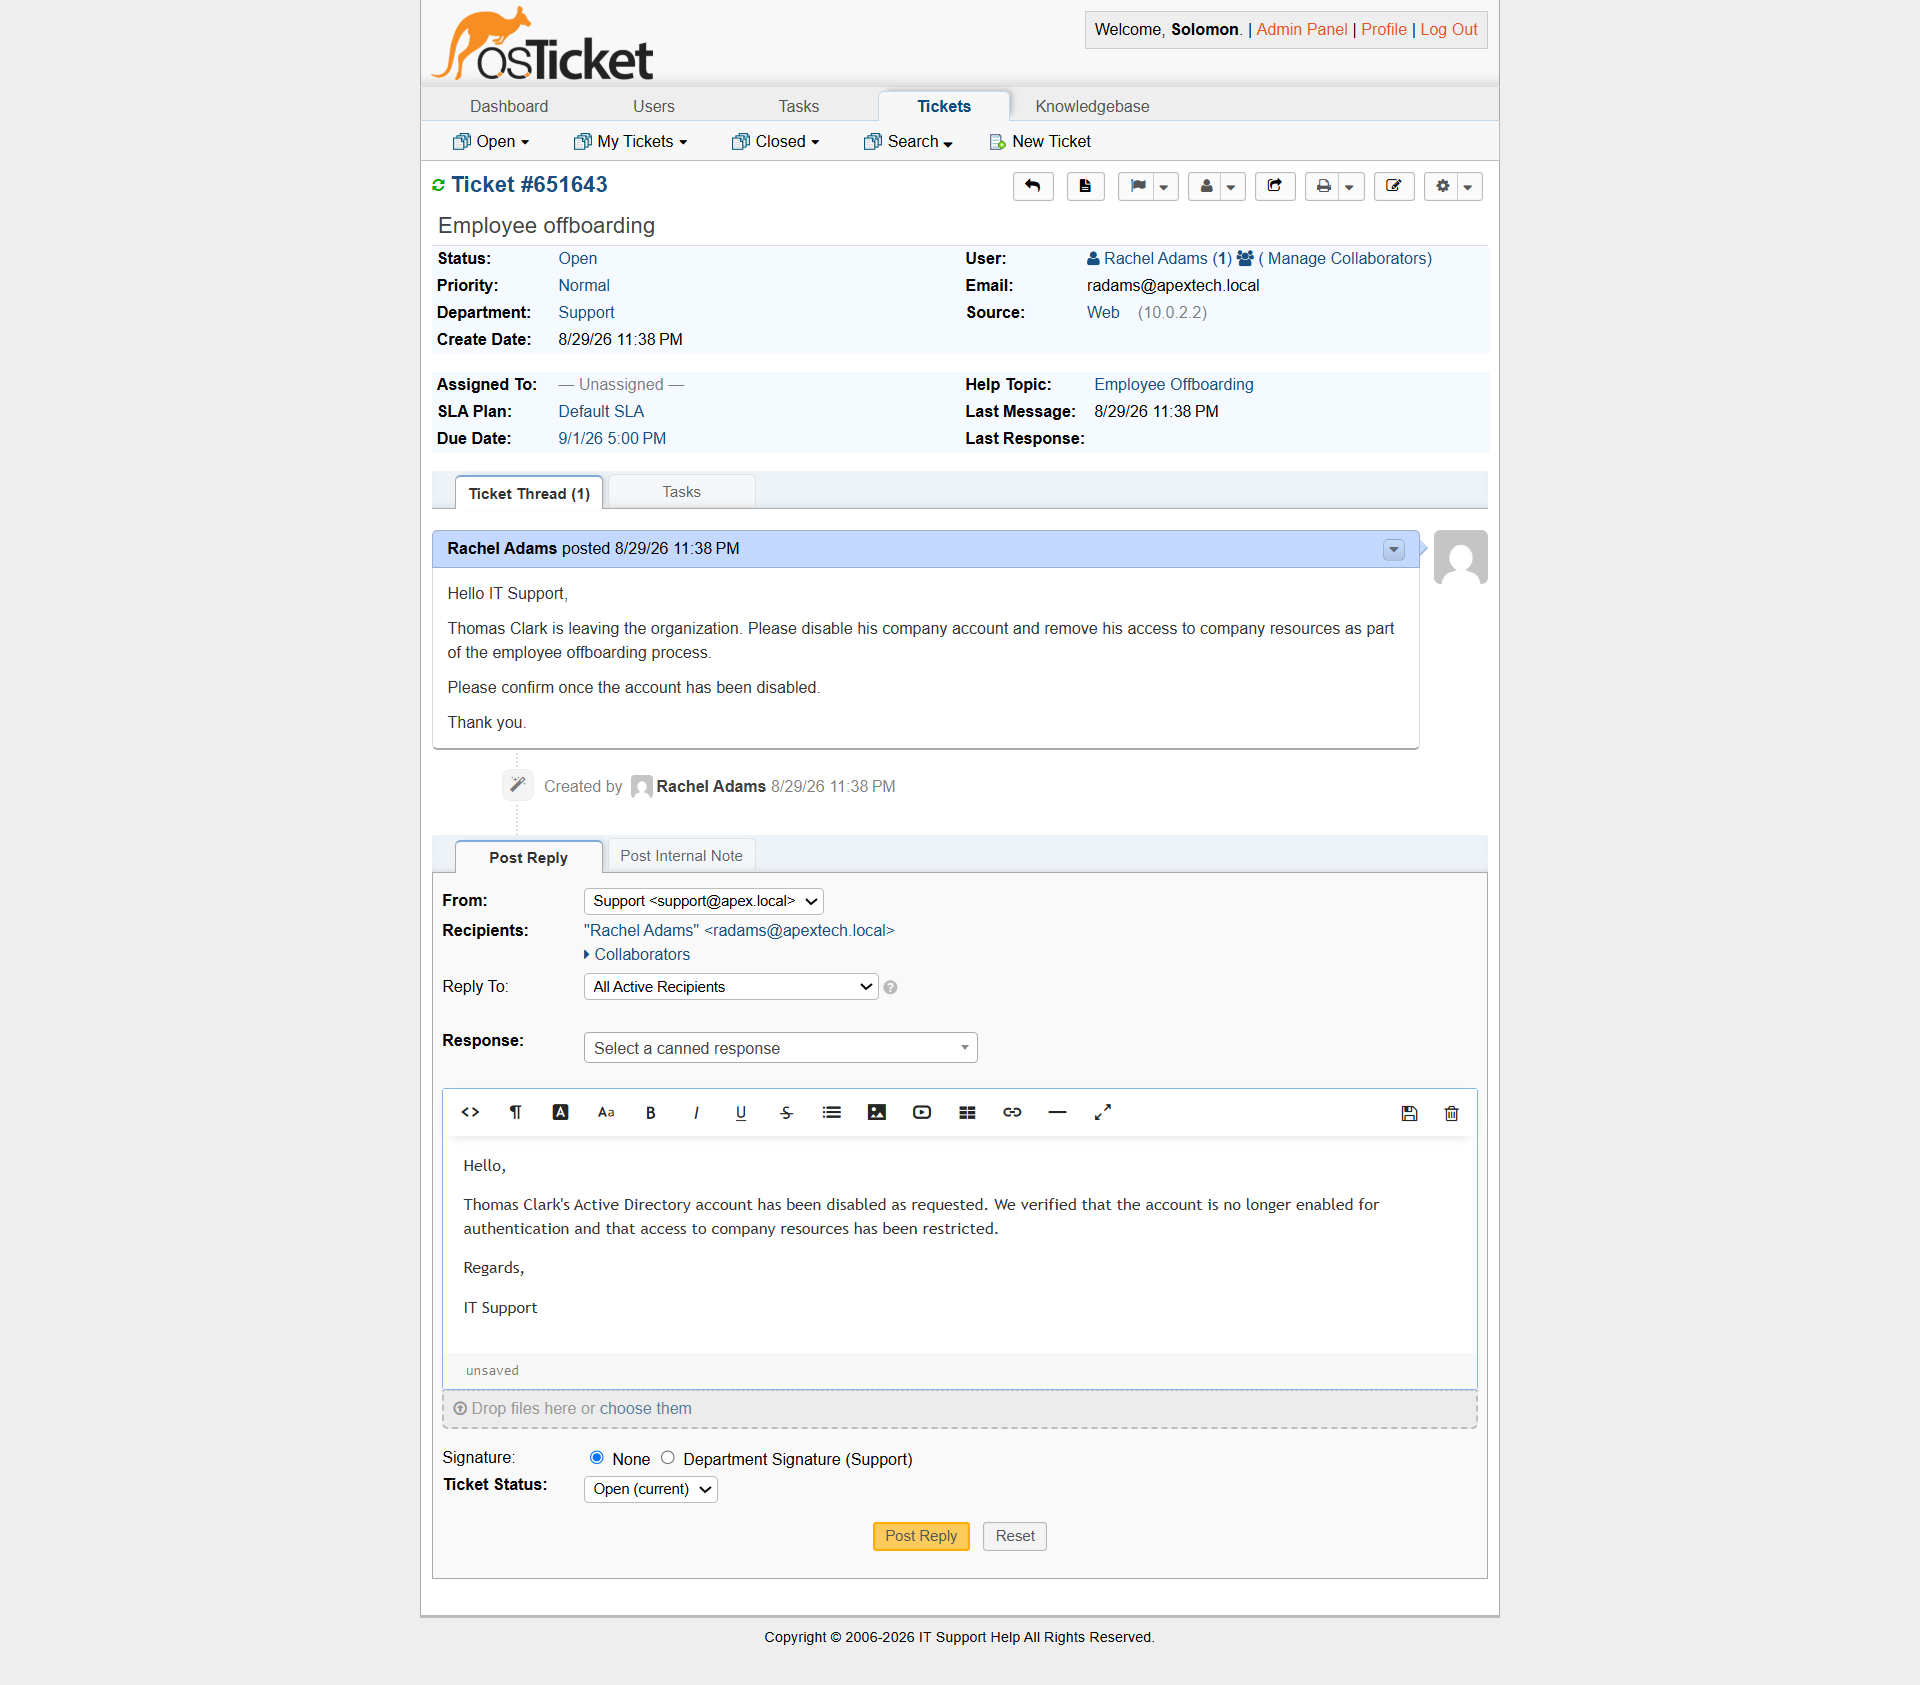
Thomas's employee-offboarding ticket showing the completed resolution and closure.
The user request was then closed after the required technical actions had been verified.
Ticket Workflow
Thomas
   │
   ▼
Employee Offboarding Request
   │
   ▼
osTicket Ticket Submitted
   │
   ▼
Active Directory Account Verified
   │
   ▼
Account Disabled
   │
   ▼
Authentication Blocked
   │
   ▼
Account Moved to Disabled Users OU
   │
   ▼
My Response
   │
   ▼
Ticket Closed